

Apache Nifi 2.2.0 version Untrusted proxy error
I set up a 4-node NiFi cluster and generated certificates. When I try to log in using my certificate user nifi_admin, I get the error:
"An unexpected error has occurred. Please check the logs for additional details."
When I checked the logs, I saw that the nodes in the cluster were encountering the following errors when trying to connect to the coordinator node:
The node I connect to the interface: https://vtmrt3anifit01.x.com:8443/nifi/
The error received in the nifi-user.log file on this machine is as follows:
| ERROR [NiFi Web Server-221] o.a.nifi.web.api.config.ThrowableMapper An unexpected error has occurred: java.io.UncheckedIOException: Read Current User Entity failed. Returning Internal Server Error response. java.io.UncheckedIOException: Read Current User Entity failed at org.apache.nifi.web.api.FlowResource.readReplicatedCurrentUserEntity(FlowResource.java:446) at org.apache.nifi.web.api.FlowResource.getCurrentUser(FlowResource.java:421) at java.base/jdk.internal.reflect.DirectMethodHandleAccessor.invoke(DirectMethodHandleAccessor.java:103) at java.base/java.lang.reflect.Method.invoke(Method.java:580) at org.glassfish.jersey.server.model.internal.ResourceMethodInvocationHandlerFactory.lambda$static$0(ResourceMethodInvocationHandlerFactory.java:52) at org.glassfish.jersey.server.model.internal.AbstractJavaResourceMethodDispatcher$1.run(AbstractJavaResourceMethodDispatcher.java:146) at org.glassfish.jersey.server.model.internal.AbstractJavaResourceMethodDispatcher.invoke(AbstractJavaResourceMethodDispatcher.java:189) . . Caused by: com.fasterxml.jackson.core.JsonParseException: Unrecognized token 'Authentication': was expecting (JSON String, Number, Array, Object or token 'null', 'true' or 'false') at [Source: REDACTED (`StreamReadFeature.INCLUDE_SOURCE_IN_LOCATION` disabled); line: 1, column: 16] at com.fasterxml.jackson.core.JsonParser._constructError(JsonParser.java:2584) at com.fasterxml.jackson.core.JsonParser._constructReadException(JsonParser.java:2610) |
The error received in the nifi-user.log file of other nodes in the cluster is as follows:
| WARN [NiFi Web Server-37] o.a.n.w.s.NiFiAuthenticationFilter Authentication Failed 10.84.2.184 GET https://vtmrt3anifit01.x.com:8443/nifi-api/flow/current-user [Untrusted proxy CN=vtmrt3anifit04.x.com, OU=NIFI] |
nifi.properties
. nifi.sensitive.props.key=6y3hk3TWqOV0E2B1AHHikAqKH8lbqo84 nifi.sensitive.props.algorithm=NIFI_PBKDF2_AES_GCM_256 nifi.security.autoreload.enabled=false nifi.security.autoreload.interval=10 secs nifi.security.keystore=/data/cert/keystore.jks nifi.security.keystoreType=jks nifi.security.keystorePasswd=UuW0OHTYY+e9OAM9Gs4MTjbR9KF7BWZ7yPZ09FB5lC0 nifi.security.keyPasswd=UuW0OHTYY+e9OAM9Gs4MTjbR9KF7BWZ7yPZ09FB5lC0 nifi.security.truststore=/data/cert/truststore.jks nifi.security.truststoreType=jks nifi.security.truststorePasswd=1rAfyXpFQvaPys8DCj0+YSH9n4hKSHT4Do0yErt/5ZM . . nifi.web.https.host=vtmrt3anifit01.x.com nifi.web.https.port=8443 nifi.web.proxy.host=vtmrt3anifit01.x.com:8443,vtmrt3anifit02.x.com:8443,vtmrt3anifit03.x.com:8443,vtmrt3anifit04.x.com:8443
|
authorizers.xml: (It is arranged in the same way for all nodes.)
<authorizers> <userGroupProvider> <identifier>file-user-group-provider</identifier> <class>org.apache.nifi.authorization.FileUserGroupProvider</class> <property name="Users File">/data/nifi-2.2.0/conf/users.xml</property> <property name="Legacy Authorized Users File"></property> <property name="Initial User Identity 0">CN=nifi_admin</property> <property name="Initial User Identity 1">CN=vtmrt3anifit01.x.com, OU=NIFI</property> <property name="Initial User Identity 2">CN=vtmrt3anifit02.x.com, OU=NIFI</property> <property name="Initial User Identity 3">CN=vtmrt3anifit03.x.com, OU=NIFI</property> <property name="Initial User Identity 4">CN=vtmrt3anifit04.x.com, OU=NIFI</property> </userGroupProvider> <accessPolicyProvider> <identifier>file-access-policy-provider</identifier> <class>org.apache.nifi.authorization.FileAccessPolicyProvider</class> <property name="User Group Provider">file-user-group-provider</property> <property name="Authorizations File">/data/nifi-2.2.0/conf/authorizations.xml</property> <property name="Initial Admin Identity">CN=nifi_admin</property> <property name="Legacy Authorized Users File"></property> <property name="Initial User Identity 1">CN=vtmrt3anifit01.x.com, OU=NIFI</property> <property name="Initial User Identity 2">CN=vtmrt3anifit02.x.com, OU=NIFI</property> <property name="Initial User Identity 3">CN=vtmrt3anifit03.x.com, OU=NIFI</property> <property name="Initial User Identity 4">CN=vtmrt3anifit04.x.com, OU=NIFI</property> <property name="Node Group"></property> </accessPolicyProvider> <authorizer> <identifier>managed-authorizer</identifier> <class>org.apache.nifi.authorization.StandardManagedAuthorizer</class> <property name="Access Policy Provider">file-access-policy-provider</property> </authorizer> </authorizers>
|
nifi_admin.p12

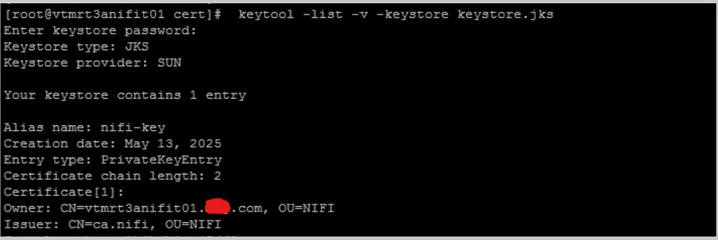
vtmrt3anifit01.x.com keystore.jks
I would appreciate your assistance on this matter.


