somesh
Gold ⭐️
May 4, 2021
Solved

Configured Ranger with AD/LDAP but not able to sync users and groups from AD.

Hi,
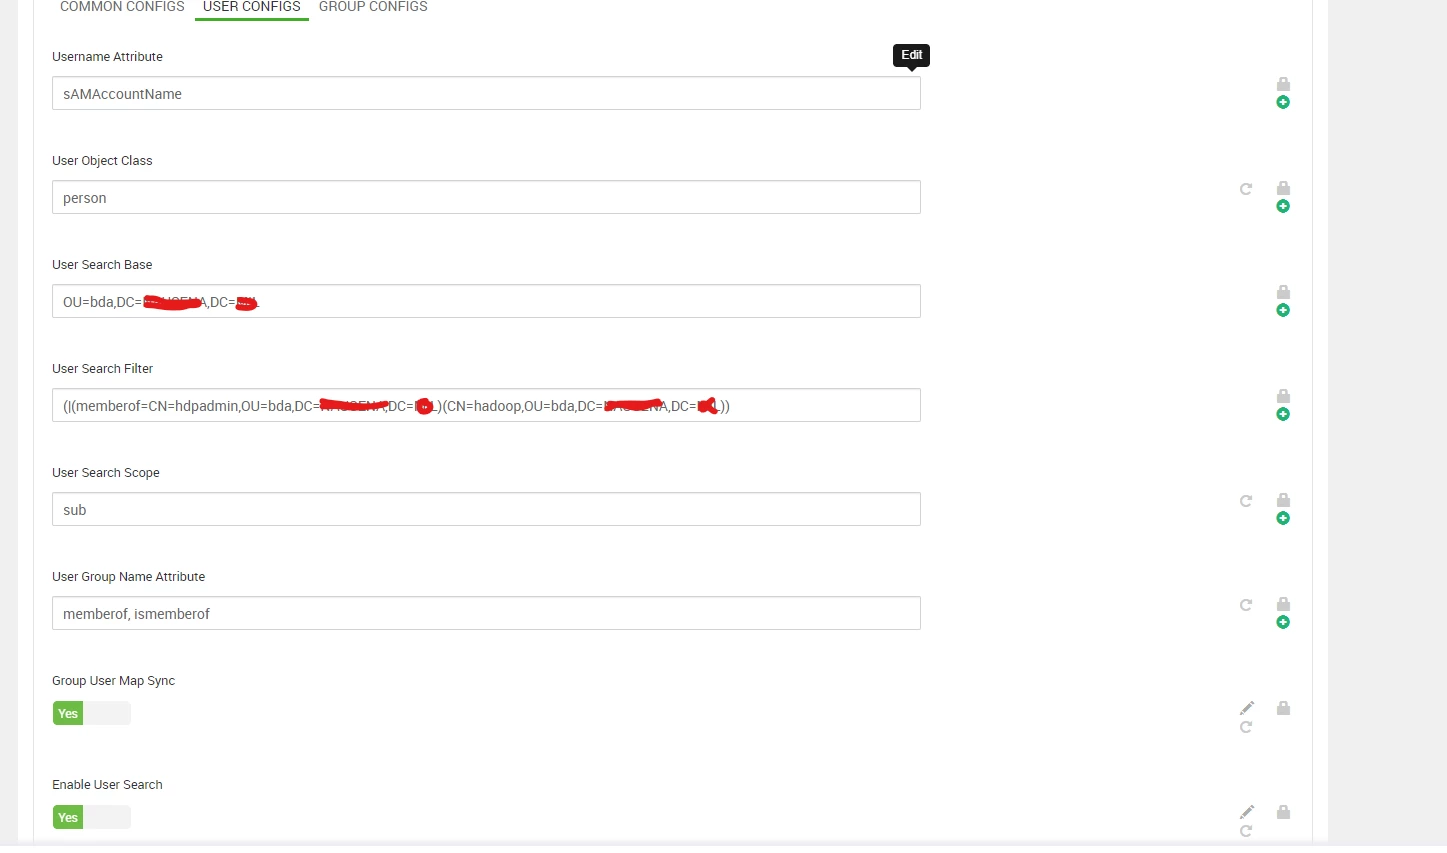
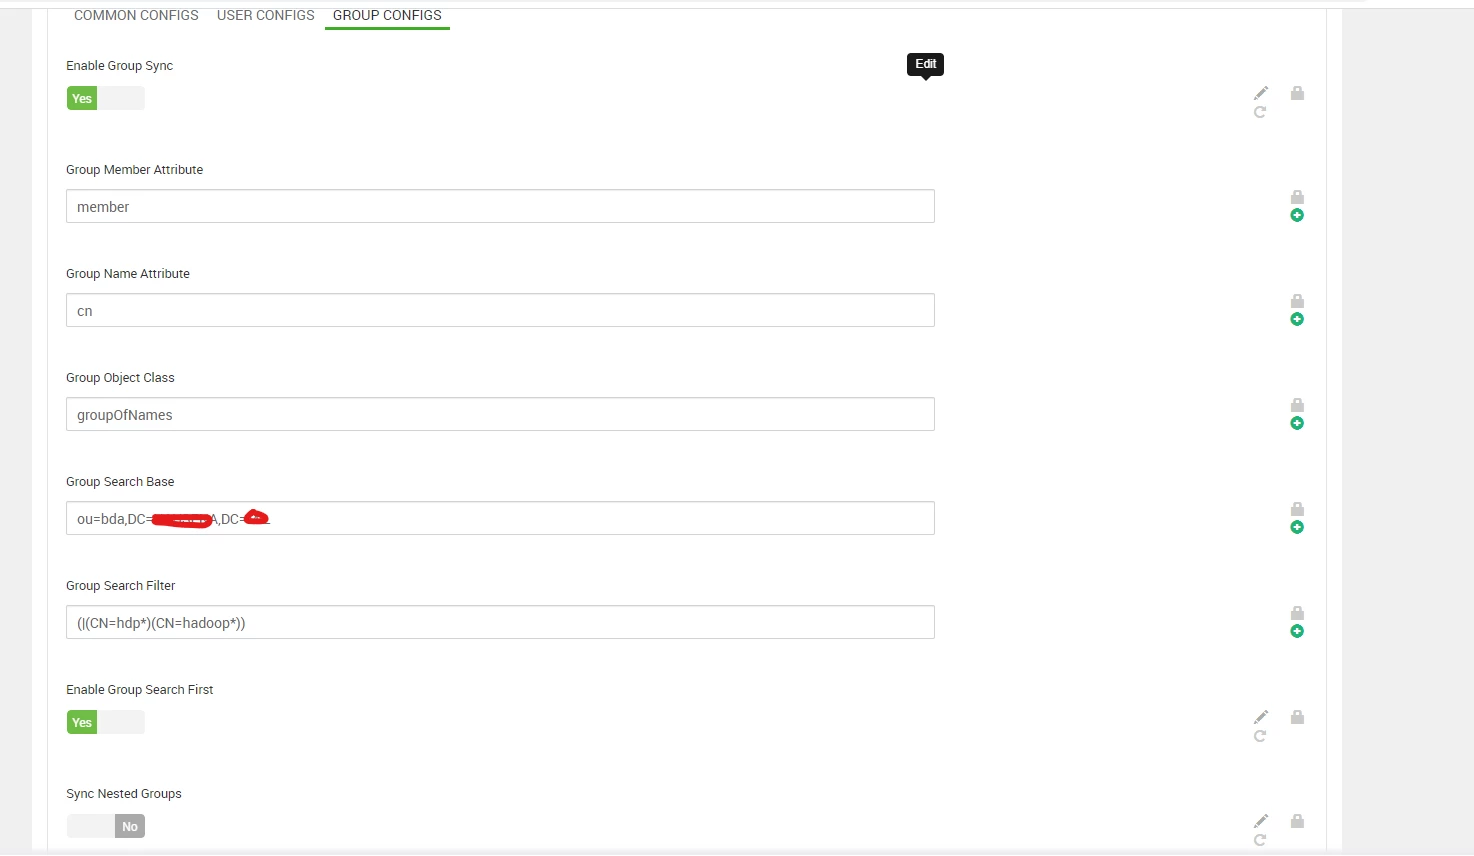
I have configured Ranger with AD for user and group sync but not able to see the users in the Ranger. Ldapsearch  is working fine and able to retrieve the users from group hdpadmin. Please find below snap for the user configuration.
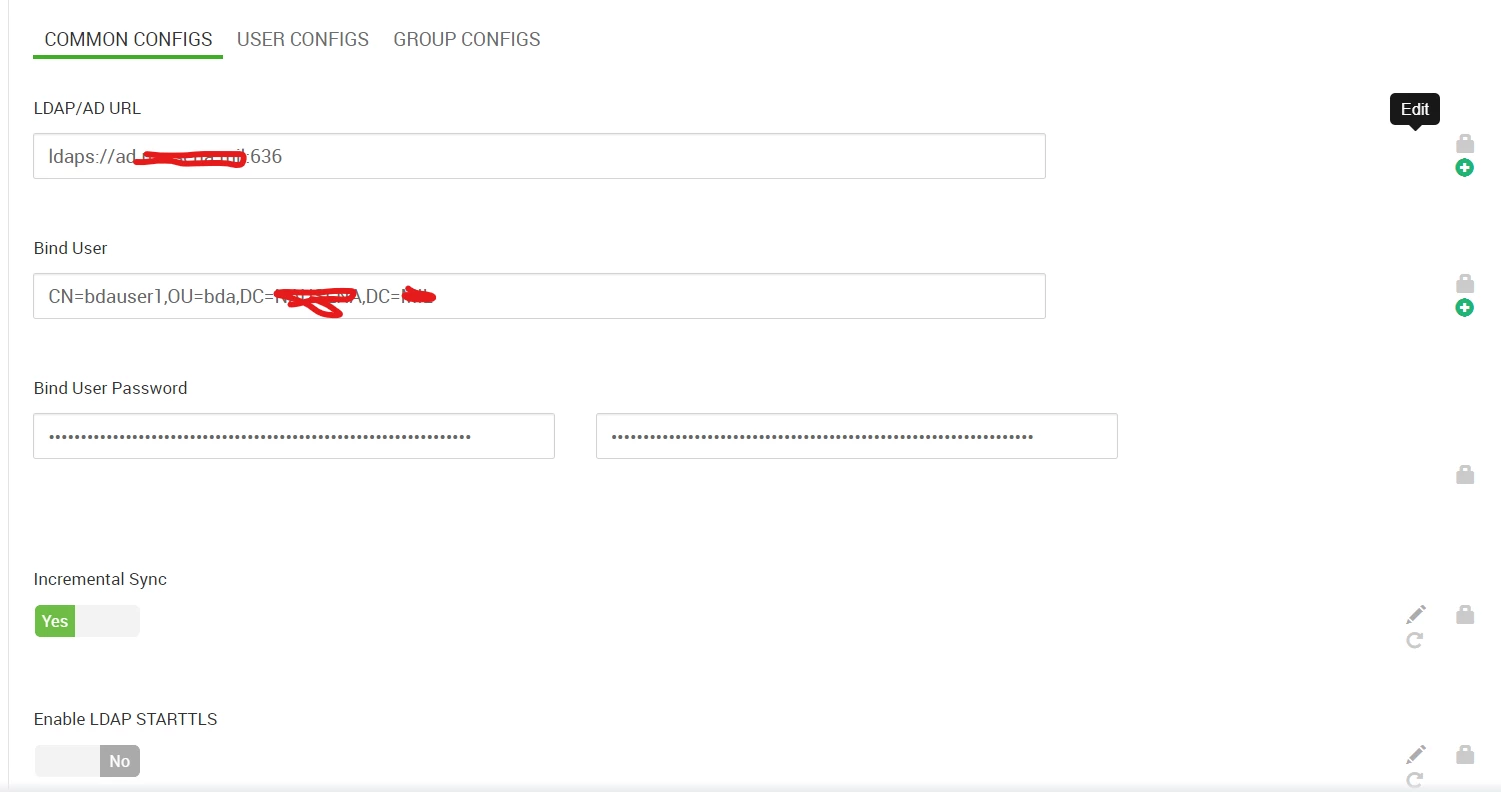
Common ConfigCommon ConfigUser ConfigUser ConfigGroup ConfigGroup Config


somesh
someshAnswer
Gold ⭐️
May 5, 2021

Able to retrieved the groups and users from that group by changing the parameters as per below link. 


https://community.cloudera.com/t5/Support-Questions/LDAP-AD-users-not-appearing-in-Ranger/m-p/285175#M211652

3 replies

Scharan
Gold ⭐️
Gold ⭐️
May 5, 2021

@somesh Can you try syncing the users by disabling "Enable Group Search First"


Translate
somesh
someshAuthor
Gold ⭐️
May 5, 2021

@Scharan ,the users are not syncing by disabling "Enable Group Search First". Please find the below configuration.


ldapUrl: ldap://ad.xxx.xxx:389,
ldapBindDn: CN=user1,OU=bda,DC=HWX,DC=COM,
ldapBindPassword: ***** ,
ldapAuthenticationMechanism: simple,
searchBase: dc=hadoop,dc=apache,dc=org,
userSearchBase: [OU=bda,DC=HWX,DC=COM],
userSearchScope: 2,
userObjectClass: (|(objectClass=person)(objectClass=user)(objectClass=top)),
userSearchFilter: (|(objectClass=person)(objectClass=user)),
extendedUserSearchFilter: (&(objectclass=(|(objectClass=person)(objectClass=user)(objectClass=top)))(|(objectClass=person)(objectClass=user))),
userNameAttribute: sAMAccountName,
userSearchAttributes: [sAMAccountName, memberof, ismemberof],
userGroupNameAttributeSet: [memberof, ismemberof],
pagedResultsEnabled: true,
pagedResultsSize: 500,
groupSearchEnabled: false,
groupSearchBase: [CN=hdpadmin,OU=bda,DC=HWX,DC=COM],
groupSearchScope: 2,
groupObjectClass: hdpadmin,
groupSearchFilter: (|(objectClass=person)(objectClass=user)),
extendedGroupSearchFilter: (&(objectclass=hdpadmin)(|(objectClass=person)(objectClass=user))(|(member={0})(member={1}))),
extendedAllGroupsSearchFilter: (&(objectclass=hdpadmin)(|(objectClass=person)(objectClass=user))),
groupMemberAttributeName: member,
groupNameAttribute: hdpadmin, groupSearchAttributes: [hdpadmin, member],
groupUserMapSyncEnabled: false, groupSearchFirstEnabled: false, userSearchEnabled: true,
ldapReferral: follow

Translate
somesh
someshAuthorAnswer
Gold ⭐️
May 5, 2021

Able to retrieved the groups and users from that group by changing the parameters as per below link. 


https://community.cloudera.com/t5/Support-Questions/LDAP-AD-users-not-appearing-in-Ranger/m-p/285175#M211652

Translate