
Platinum ⭐️⭐️
November 9, 2023
Solved

JWT token issue while setting up three node NIFI cluster

I have created a three node NIFI cluster and the embedded zookeeper is set up and all the three nodes are communicating with each other through heartbeats but when I try to access the NIFI UI I am getting the below error:
Unauthorized error="invalid_token", error_description="An error occurred while attempting to decode the Jwt: Signed JWT rejected: Another algorithm expected, or no matching key(s) found", error_uri="https://tools.ietf.org/html/rfc6750#section-3.1"
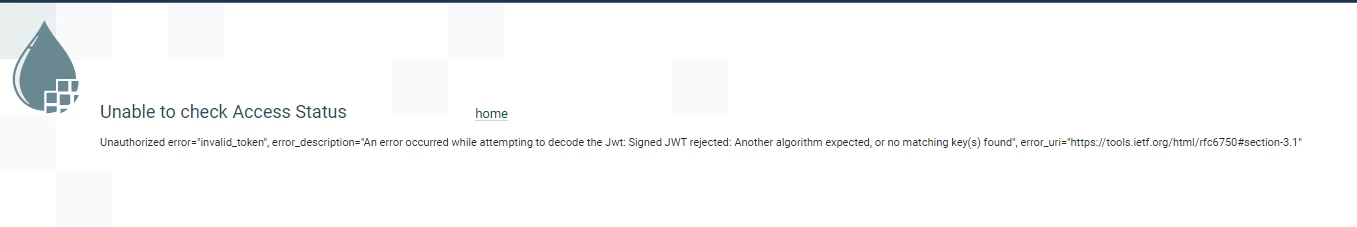
jwt error.png

How do I fix this issue?

MattWho
MattWhoAnswer
Titanium ⭐️⭐️⭐️
December 1, 2023

@Former Member 

Do you have a load balancer in front of your NiFi Cluster?
If so, the load balancer needs to be configured to use session persistence (also known as sticky sessions).  That is because when you access node 1 for example and authenticate your user that token is only valid for that specific node (there is a client token and a matching server side key).  If subsequent request/redirect is sent to a different node by the load balancer the node is going to be missing the matching server side key and reject the client token.

Sharing more details about your NiFi security setup and Apache NiFi version is also valuable to those who may provide suggestion in the community.

If you found any of the suggestions/solutions provided helped you with your issue, please take a moment to login and click "Accept as Solution" on one or more of them that helped.

Thank you,
Matt

3 replies

dileepkumar_upp
Silver ⭐️⭐️
November 30, 2023

@Former Member , issue has been fixed?

if yes, can you share the details to resolve

Translate
MattWho
Titanium ⭐️⭐️⭐️
MattWhoAnswer
Titanium ⭐️⭐️⭐️
December 1, 2023

@Former Member 

Do you have a load balancer in front of your NiFi Cluster?
If so, the load balancer needs to be configured to use session persistence (also known as sticky sessions).  That is because when you access node 1 for example and authenticate your user that token is only valid for that specific node (there is a client token and a matching server side key).  If subsequent request/redirect is sent to a different node by the load balancer the node is going to be missing the matching server side key and reject the client token.

Sharing more details about your NiFi security setup and Apache NiFi version is also valuable to those who may provide suggestion in the community.

If you found any of the suggestions/solutions provided helped you with your issue, please take a moment to login and click "Accept as Solution" on one or more of them that helped.

Thank you,
Matt

Translate
Sullaka
Silver ⭐️
September 24, 2024

I too faced the same issue, I enabled stickyness on my Load balancer targetGroup and it worked!!

Hompe thims hempls...

Translate

