

Solved
Knox authentication with PAM
Hello Team,
I have an issue with setting the Knox authentication with PAM. I have the default login in /etc/pam.d/
$ cat /etc/pam.d/login
#%PAM-1.0
auth [user_unknown=ignore success=ok ignore=ignore default=bad] pam_securetty.so
auth       substack     system-auth
auth       include      postlogin
account    required     pam_nologin.so
account    include      system-auth
password   include      system-auth
# pam_selinux.so close should be the first session rule
session    required     pam_selinux.so close
session    required     pam_loginuid.so
session    optional     pam_console.so
# pam_selinux.so open should only be followed by sessions to be executed in the user context
session    required     pam_selinux.so open
session    required     pam_namespace.so
session    optional     pam_keyinit.so force revoke
session    include      system-auth
session    include      postlogin
-session   optional     pam_ck_connector.so
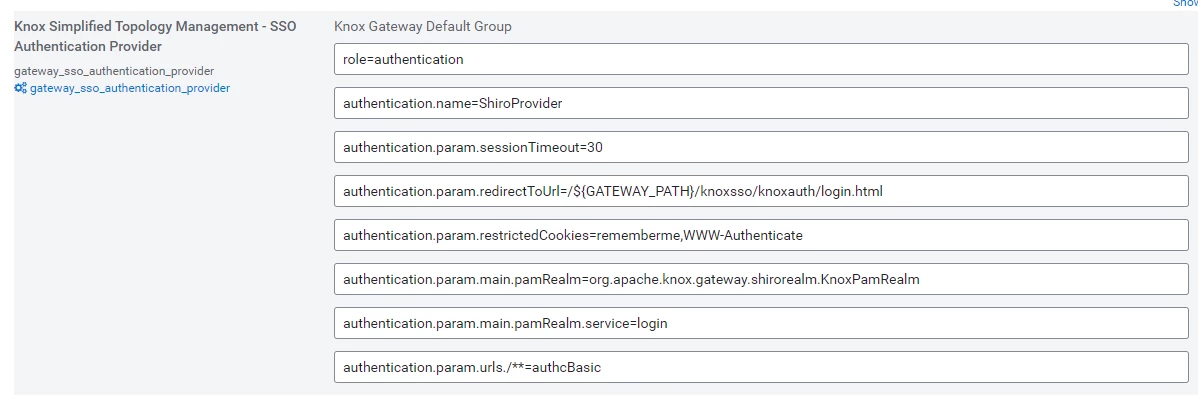
Knox-sso looks as following (the default one)
I created a user named - test with a password. I tried to access the Knox Gateway UI but I get the issue.
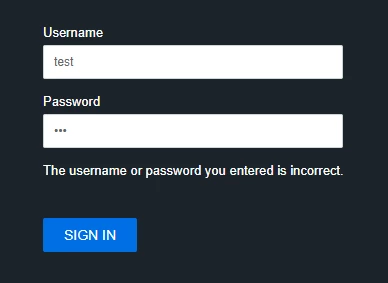
The Knox Gateway log says:
(KnoxPamRealm.java:handleAuthFailure(170)) - Shiro unable to login: null
Note: I am using CDP 7.1.6 and I can login to my host (where Knox Gateway is installed) using the test user. Also, there's no Kerberos setup.
Please share if there's something that needs to be adjusted.
Best Regards
Sayed


