Solved
NIFI LDAP Groups not showing the users
Hi ,
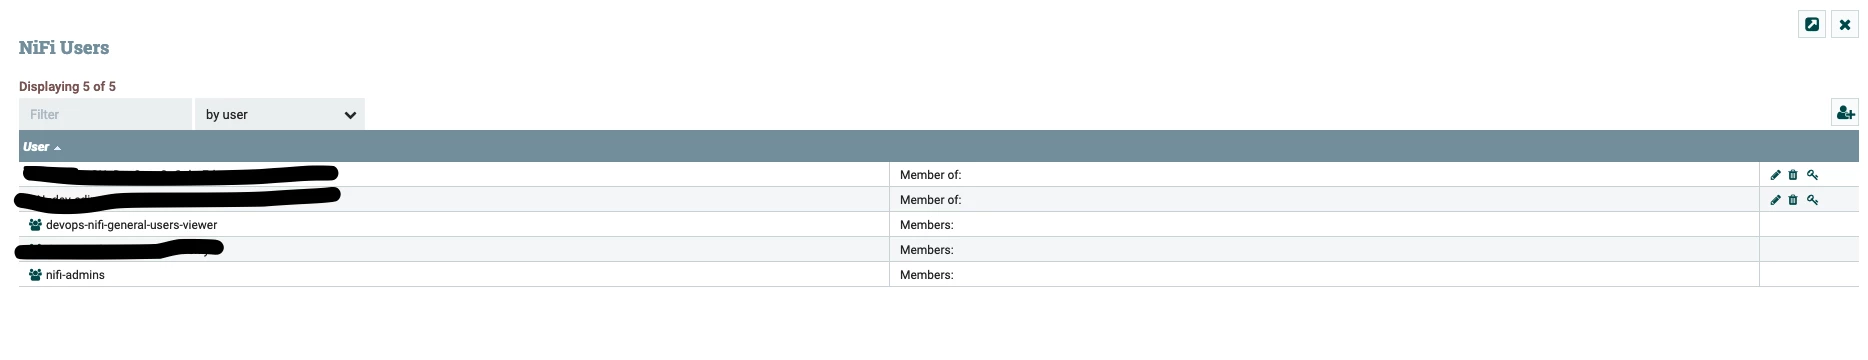
I have an issue integrating NIFI with LDAP groups, I created two groups in LDAP and added users to those groups but the NIFI shows those groups empty without users. I started DEBUG level, and I can see from the debug the following message
devops-nifi-general-users-viewer contains member CN=Edi,OU=XX,OU=XX,OU=XXX,OU=XXX,OU=XXX,OU=XXX,OU=XXXX,DC=XXXX,DC=local but that user was not found while searching users. This may be due to a misconfiguration or it's possible the user is not a NiFi user. Ignoring group membership.
Any suggestion on what can be the issue ? why can't I see the users in the groups?
(attaching the configuration files )
full log messages
2023-08-14 14:52:11,537 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider devops-nifi-general-users-viewer contains member CN=Edi,OU=XX,OU=XX,OU=XXX,OU=XXX,OU=XXX,OU=XXX,OU=XXXX,DC=XXXX,DC=local but that user was not found while searching users. This may be due to a misconfiguration or it's possible the user is not a NiFi user. Ignoring group membership.
2023-08-14 14:52:11,556 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider nifi-admins contains member CN=Edi,OU=XX,OU=XXX,OU=XXX,OU=XXX,OU=XXX,OU=XX,OU=XX,DC=XX,DC=local but that user was not found while searching users. This may be due to a misconfiguration or it's possible the user is not a NiFi user. Ignoring group membership.
2023-08-14 14:52:11,559 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider -------------------------------------
2023-08-14 14:52:11,559 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider Loaded the following users from LDAP:
2023-08-14 14:52:11,559 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider --------------------------------------
2023-08-14 14:52:11,559 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider Loaded the following groups from LDAP:
2023-08-14 14:52:11,560 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider  - identifier[606a319b-d23f-327b-bd0e-069f1019a42b], name[devops-nifi-general-users-viewer], users[]
2023-08-14 14:52:11,560 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider  - identifier[fd4aa4e9-598f-39a5-b218-83801e57978f], name[nifi-admins], users[]
2023-08-14 14:52:11,561 DEBUG [main] o.a.n.ldap.tenants.LdapUserGroupProvider --------------------------------------
authorizers.xml
<authorizers>
    <userGroupProvider>
        <identifier>file-user-group-provider</identifier>
        <class>org.apache.nifi.authorization.FileUserGroupProvider</class>
        <property name="Users File">./conf/users.xml</property>
        <property name="Legacy Authorized Users File"></property>
        <property name="Initial User Identity 1">CN=XXX</property>
        <property name="Initial User Identity 2">CN=XXX</property>
    </userGroupProvider>


    <userGroupProvider>
        <identifier>ldap-user-group-provider</identifier>
        <class>org.apache.nifi.ldap.tenants.LdapUserGroupProvider</class>
        <property name="Page Size"></property>
        <property name="Sync Interval">30 mins</property>
        <property name="Group Membership - Enforce Case Sensitivity">false</property>

        <property name="Authentication Strategy">SIMPLE</property>
        <property name="Manager DN">XXX</property>
        <property name="Manager Password">XXX</property>
        <property name="TLS - Keystore"></property>
        <property name="TLS - Keystore Password"></property>
        <property name="TLS - Keystore Type"></property>
        <property name="TLS - Truststore"></property>
        <property name="TLS - Truststore Password"></property>
        <property name="TLS - Truststore Type"></property>
        <property name="TLS - Client Auth"></property>
        <property name="TLS - Protocol"></property>
        <property name="TLS - Shutdown Gracefully"></property>
        <property name="Referral Strategy">FOLLOW</property>
        <property name="Connect Timeout">10 secs</property>
        <property name="Read Timeout">10 secs</property>
        <property name="Url">ldap:XXX</property>
        <property name="User Search Base">XXX</property>
        <property name="User Object Class">person</property>
        <property name="User Search Scope">ONE_LEVEL</property>
        <property name="User Search Filter">(sAMAccountName={0})</property>
        <property name="User Identity Attribute">sAMAccountName</property>
        <property name="User Group Name Attribute"></property>
        <property name="Authentication Expiration">12 hours</property>

        <property name="User Group Name Attribute - Referenced Group Attribute"></property>
        <property name="Group Search Base">XXX</property>
        <property name="Group Object Class">group</property>
        <property name="Group Search Scope">ONE_LEVEL</property>
        <property name="Group Search Filter"></property>
        <property name="Group Name Attribute">cn</property>
        <property name="Group Member Attribute">member</property>
        <property name="Group Member Attribute - Referenced User Attribute"></property>

    </userGroupProvider>


      <userGroupProvider>
        <identifier>composite-user-group-provider</identifier>
        <class>org.apache.nifi.authorization.CompositeConfigurableUserGroupProvider</class>
        <property name="Configurable User Group Provider">file-user-group-provider</property>
        <property name="User Group Provider 1">ldap-user-group-provider</property>
    </userGroupProvider>

    <accessPolicyProvider>
        <identifier>file-access-policy-provider</identifier>
        <class>org.apache.nifi.authorization.FileAccessPolicyProvider</class>
        <property name="User Group Provider">composite-user-group-provider</property>
        <property name="Authorizations File">./conf/authorizations.xml</property>
        <property name="Initial Admin Identity">XXX</property>
        <property name="Legacy Authorized Users File"></property>

        <property name="Node Identity 1">XXX</property>
    </accessPolicyProvider>
    <authorizer>
        <identifier>managed-authorizer</identifier>
        <class>org.apache.nifi.authorization.StandardManagedAuthorizer</class>
        <property name="Access Policy Provider">file-access-policy-provider</property>
    </authorizer>
</authorizers>
nifi.properties
nifi.security.keystore=/opt/nifi/cert-all/xxx
nifi.security.keystorePasswd=xxx
nifi.security.keyPasswd=xxx
nifi.security.truststore=/opt/nifi/cert-all/xxx
nifi.security.truststoreType=jks
nifi.security.truststorePasswd=xxx
nifi.security.user.authorizer=managed-authorizer
nifi.security.allow.anonymous.authentication=false
nifi.security.user.login.identity.provider=ldap-provider
nifi.security.user.jws.key.rotation.period=PT1H
nifi.security.ocsp.responder.url=
nifi.security.ocsp.responder.certificate=