
No available buckets after secure Nifi connected to secure Nifi registry
Hello All,
I had secure Nifi and Secured Nifi-registry running on Docker.
Both share same certificates
Able to access both UI's individually.
Given static IP to Registry in Docker and subjectalternativenames with this IP while generating certificates.
Given this static_IP:<port> in registry client.
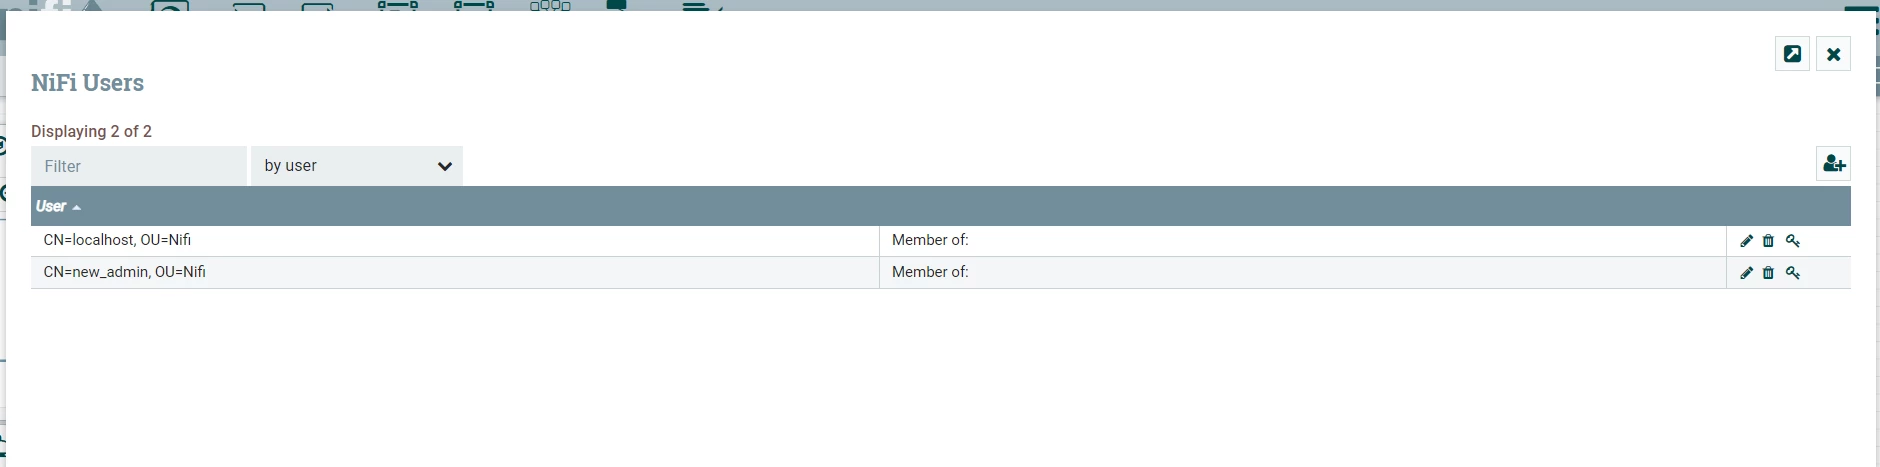
created localhost user : CN=localhost, OU=Nifi in both systems and given necessary permissions.
Created few buckets and given all necessary permissions..
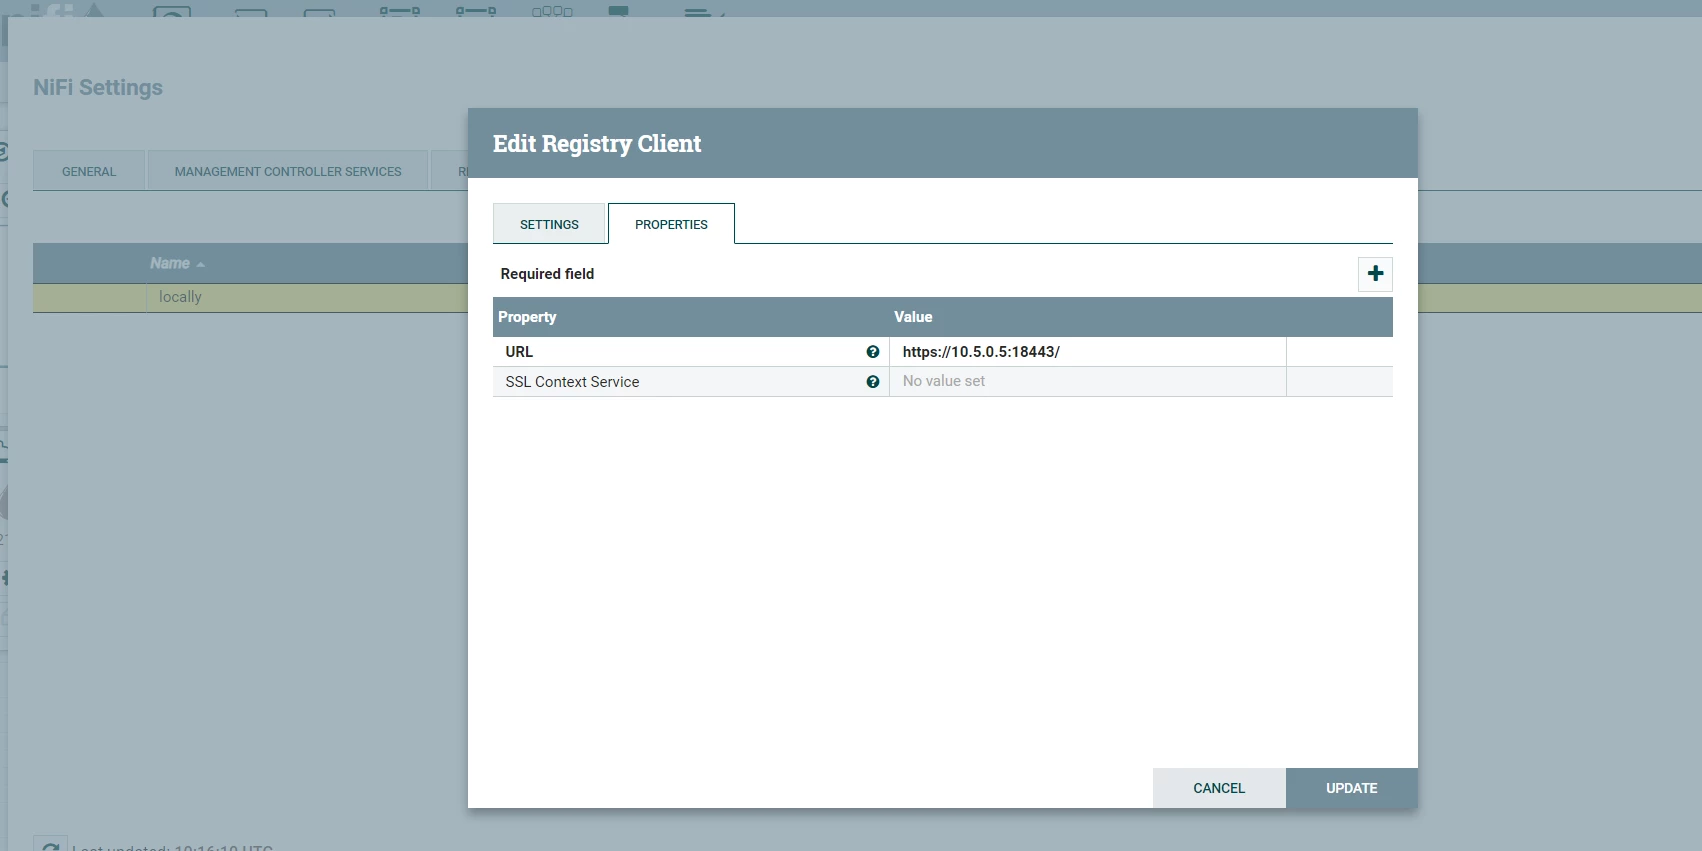
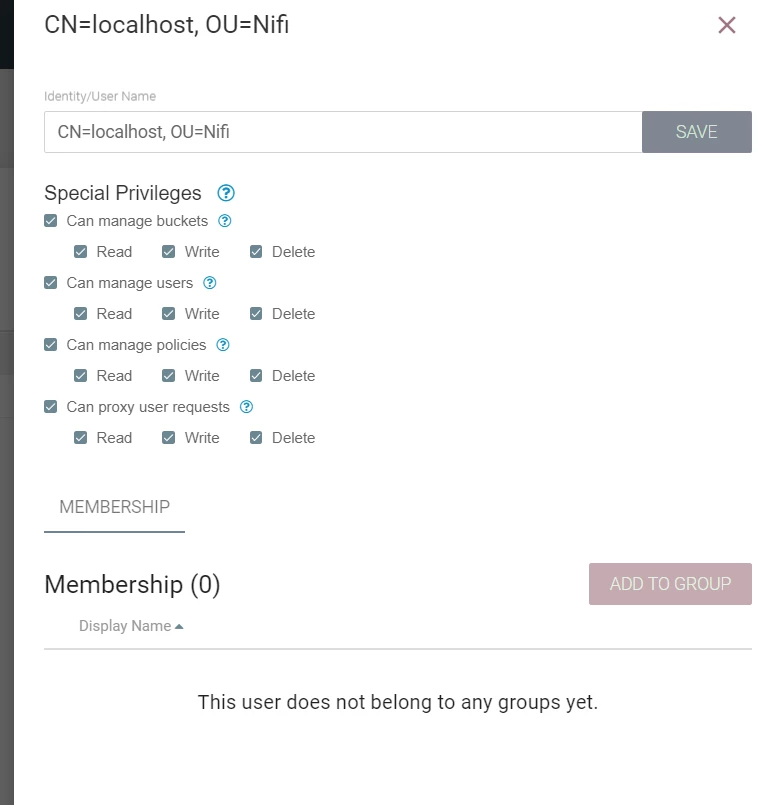
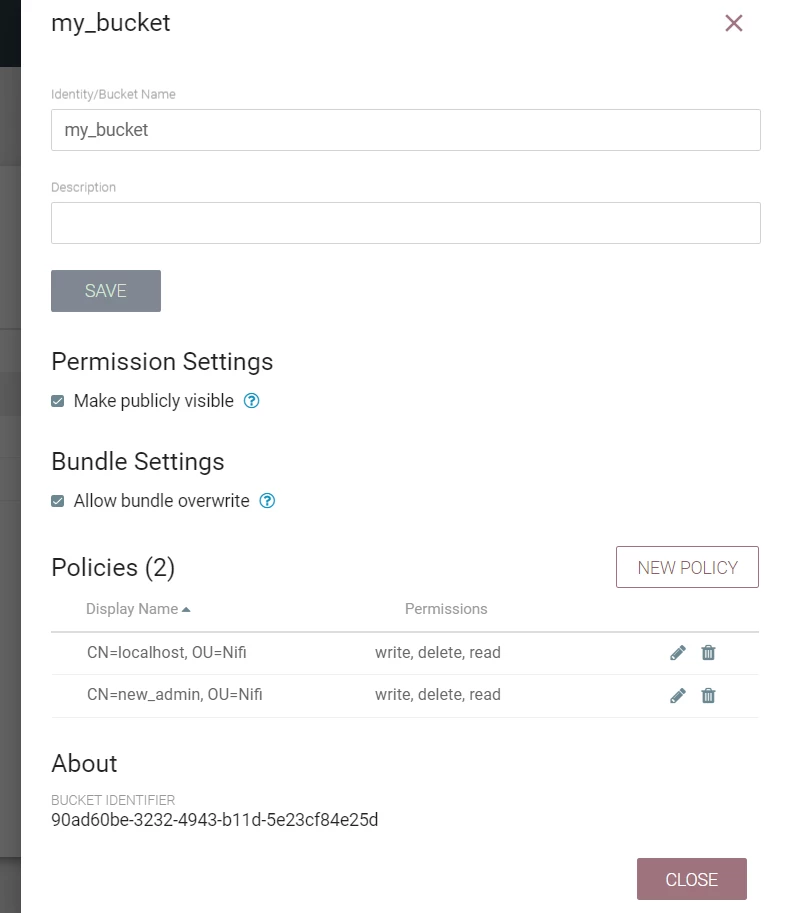
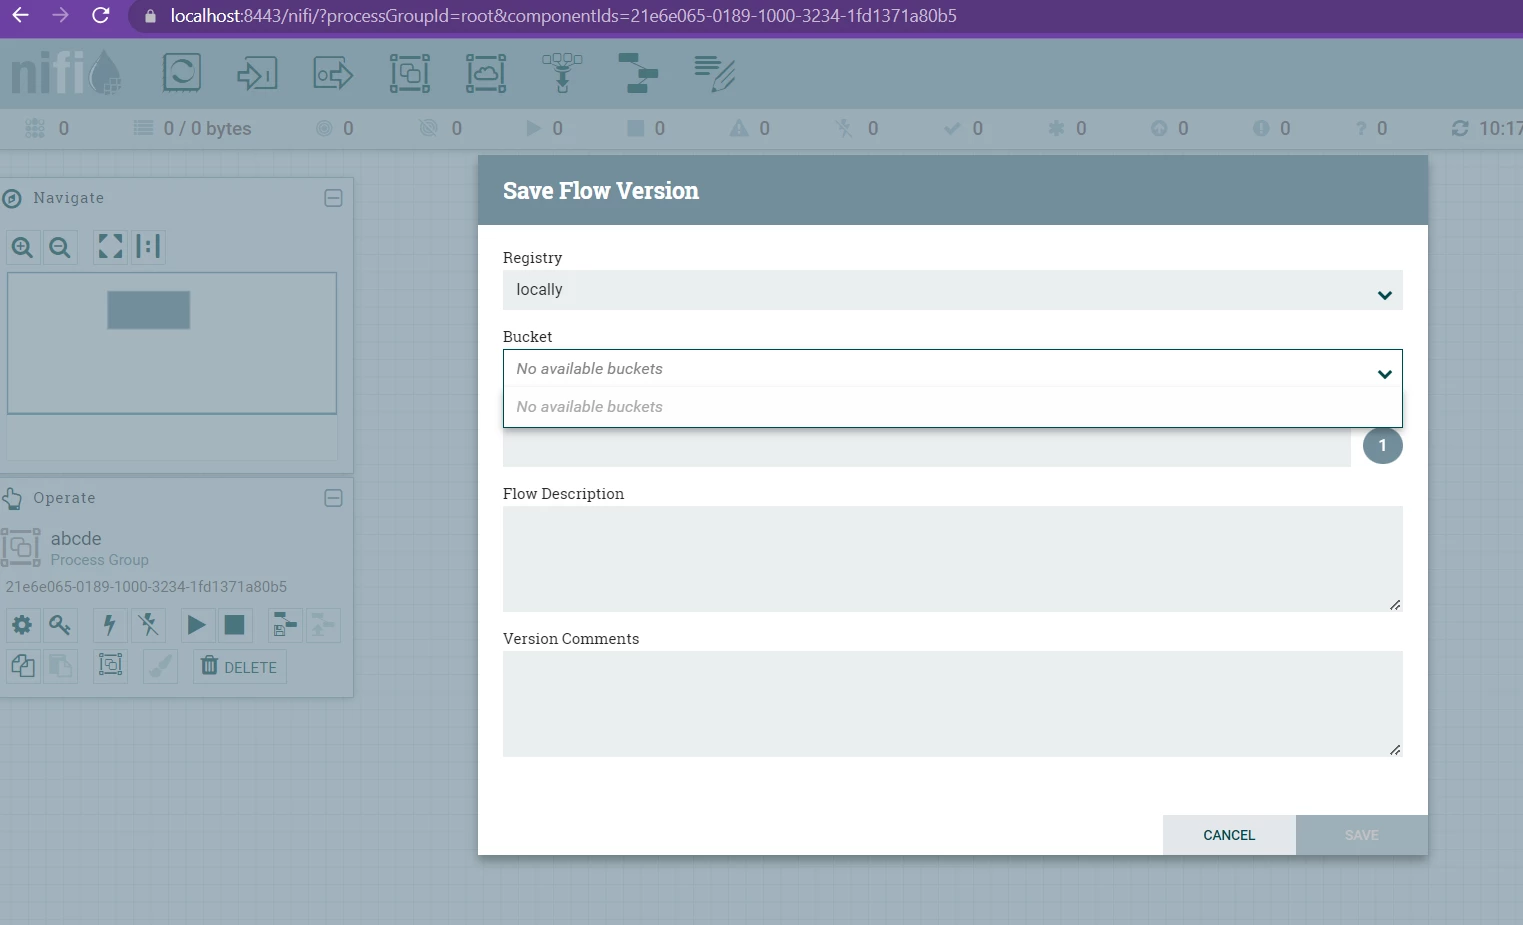
But when I try to do version control, it says no available buckets.
As i troubleshoot, I can see the logs that shows successful authorization to registry..
2023-07-05 10:25:47,312 INFO [NiFi Web Server-468] o.a.n.w.s.NiFiAuthenticationFilter Authentication Started 10.5.0.1 [CN=new_admin, OU=Nifi] GET https://localhost:8443/nifi-api/flow/registries/21d17428-0189-1000-4a0e-a91cc8cd2aa7/buckets
2023-07-05 10:25:47,312 INFO [NiFi Web Server-468] o.a.n.w.s.NiFiAuthenticationFilter Authentication Success [CN=new_admin, OU=Nifi] 10.5.0.1 GET https://localhost:8443/nifi-api/flow/registries/21d17428-0189-1000-4a0e-a91cc8cd2aa7/buckets
2023-07-05 10:26:11,541 INFO [NiFi Web Server-457] o.a.n.w.s.NiFiAuthenticationFilter Authentication Started 10.5.0.1 [CN=new_admin, OU=Nifi] GET https://localhost:8443/nifi-api/flow/process-groups/219e3cc2-0189-1000-7c6f-90a4496cf140
2023-07-05 10:26:11,541 INFO [NiFi Web Server-457] o.a.n.w.s.NiFiAuthenticationFilter Authentication Success [CN=new_admin, OU=Nifi] 10.5.0.1 GET https://localhost:8443/nifi-api/flow/process-groups/219e3cc2-0189-1000-7c6f-90a4496cf140
when i tried to open the buckets API URL (from above log) in my browser, i could get the buckets list aslo..
highlighted my buckets in Nifi-registry

I wonder why UI is not able to show the list, when Nifi's internal API call is able to fetch them correctly.
Does this indicate a bug from Nifi ? or I am missing something ?
After going through all the hurdles and still not successful with Integration, I am thingking about skipping secure installtions and just proceed with unsecure Implementations...
Because this is running in VPN on a server, I need to ssh tunnel it anyway to even access the UI. So I was thinking it is okay for unsecure Nifi UIs (as this is internal).
Please share your thoughts as well for my understanding.
Please let know if any more information is needed in this question for better understanding.
Thank You..


