

mohdriyaz
Gold ⭐️
March 12, 2024
Solved

Not able to update ParameterContent using Nifi REST API

Hello All,

I am using Nifi 2.0

I want to update existing Parameter Context using Nifi API.  For that , following API is used 

https://localhost:8443/nifi-api/parameter-contexts/2ddc0cea-018e-1000-3852-3611d730f705/update-requests

Where  "2ddc0cea-018e-1000-3852-3611d730f705" is the Id of parameter context. 
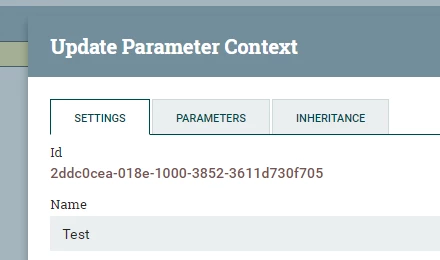
mohdriyaz_0-1710217058741.png

Issue : 

I tried to update the ParameterContext using 

https://localhost:8443/nifi-api/parameter-contexts/2ddc0cea-018e-1000-3852-3611d730f705/update-requests

but its throwing 403 error .

I updated the Request with  token (Bearer) but still getting the same error. 

Any Pointers..??

Thanks, 

Riyaz



mohdriyaz
mohdriyazAnswer
Gold ⭐️
March 19, 2024

I am able to solve the problem 

Access token Rest API generates two token (check under cookies)  - Secure-Request-Token and other is Secure-Authorization-Bearer token. 

While calling any of the other API (like creating Parameter Context or updating Parameter context)  - in Headers provide one more header "Request-Token"  with the value of  _secure-Request-Token (From cookies).

5 replies

VidyaSargur
Community Manager
Community Manager
March 12, 2024

@mohdriyaz, Welcome to our community! To help you get the best possible answer, I have tagged in our NiFi experts @cotopaul @SAMSAL @TimothySpann  who may be able to assist you further.

Please feel free to provide any additional information or details about your query, and we hope that you will find a satisfactory solution to your question.

Translate
Regards, Vidya Sargur, Community Manager Was your question answered? Make sure to mark the answer as the accepted solution. If you find a reply useful, say thanks by clicking on the thumbs up button.
ckumar
Platinum ⭐️
Platinum ⭐️
March 12, 2024

403 : Client is not authorized to make this request. 

This means you are Authenticated and since you have a valid token but you are not authorized to do this action.

to double-check if your user is Authorized, check if you can do the same action directly from NiFi UI ?  

Thank you 

Translate
mohdriyaz
mohdriyazAuthor
Gold ⭐️
March 13, 2024

@ckumar 

Yes , i am able to do the changes via Nifi UI.

Note : 

I have created the user user using following command  :  

nifi.cmd set-single-user-credentials username password


Translate
ckumar
Platinum ⭐️
Platinum ⭐️
March 14, 2024

I would further interested check nifi-user.log to see the forbidden events when you see  403 error 

Translate
mohdriyaz
mohdriyazAuthorAnswer
Gold ⭐️
March 19, 2024

I am able to solve the problem 

Access token Rest API generates two token (check under cookies)  - Secure-Request-Token and other is Secure-Authorization-Bearer token. 

While calling any of the other API (like creating Parameter Context or updating Parameter context)  - in Headers provide one more header "Request-Token"  with the value of  _secure-Request-Token (From cookies).

Translate
