

simps
Gold ⭐️
August 8, 2019
Solved

Problem starting CDSW sessions after deleting krb5.conf

We are running a non-kerberized cluster with around ten nodes. However, the workbench was displaying Kerberos configuration for Hadoop Authentication, because the host of the workbench had a krb5.conf file. As described in the docs (https://www.cloudera.com/documentation/data-science-workbench/1-5-x/topics/cdsw_kerberos.html) we stoppend the workbench, deleted the file, restarted the service. However, now we're encountering this roblem when starting new sessions on the workbench. Which configuration has to be reset to get rid of this?
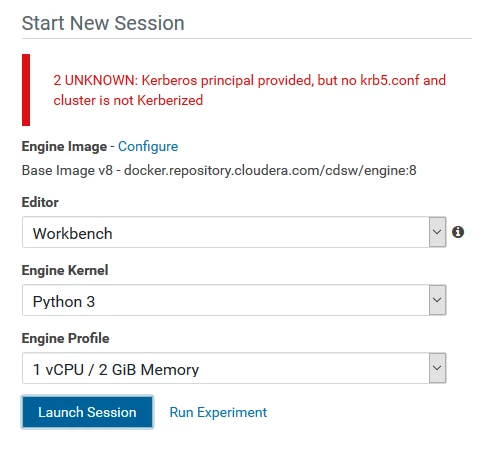

 

2019-08-08 14_11_29-New Session · simon.stemper _ Test Project · Cloudera Data Science Workbench.png

AutoIN
AutoINAnswer
Gold ⭐️⭐️
October 24, 2019

@simps In CDSW version 1.6.0 there was a wrong check in our code which failed engines if /etc/krb5.conf file was missing. We fixed it in 1.6.1. 

Fixed an issue where sessions on non-kerberized environments would throw the following error even though no principal was provided: Kerberos principal provided, but no krb5.conf and cluster is not Kerberized.

Cloudera Bug: DSE-7236


Please see if you can upgrade to this minor release or as a workaround you can place a dummy krb5.conf in /etc/ on all CDSW hosts.


Regards

Amit


4 replies

GangWar
Platinum ⭐️⭐️
Platinum ⭐️⭐️
October 15, 2019

@simps  Can you please Goto the CDSW > Account settings > Hadoop Authentication and delete the principal and credentials (password) save changes and then try to launch the session.

Translate
Cheers! Was your question answered? Make sure to mark the answer as the accepted solution. If you find a reply useful, say thanks by clicking on the thumbs up button.
simps
simpsAuthor
Gold ⭐️
October 23, 2019

Unfortunately not, because in Hadoop authentication the only field shown is to set the HADOOP_USER_NAME env variable, as shown in the screenshot:

2019-10-23 15_58_22-Hadoop Authentication · simon.stemper · Cloudera Data Science Workbench.png

I believe we started to kerberize the cluster some time ago but stopped relatively early in the process due to time constraints. Maybe a setting somewhere in the cluster is to blame?

Translate
AutoIN
Gold ⭐️⭐️
AutoINAnswer
Gold ⭐️⭐️
October 24, 2019

@simps In CDSW version 1.6.0 there was a wrong check in our code which failed engines if /etc/krb5.conf file was missing. We fixed it in 1.6.1. 

Fixed an issue where sessions on non-kerberized environments would throw the following error even though no principal was provided: Kerberos principal provided, but no krb5.conf and cluster is not Kerberized.

Cloudera Bug: DSE-7236


Please see if you can upgrade to this minor release or as a workaround you can place a dummy krb5.conf in /etc/ on all CDSW hosts.


Regards

Amit


Translate

