bananaman
Gold ⭐️
December 21, 2022
Solved

Ranger doesn't sync all users from Active Directory

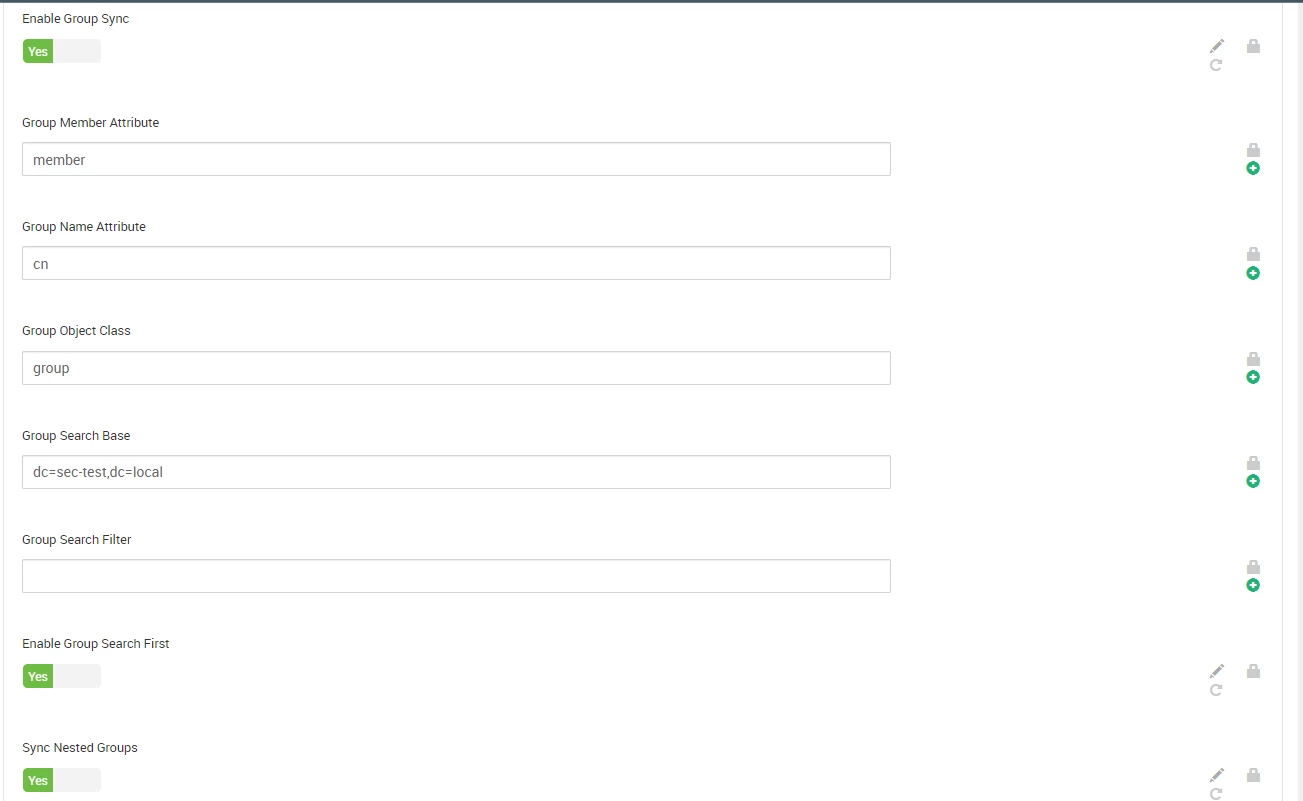
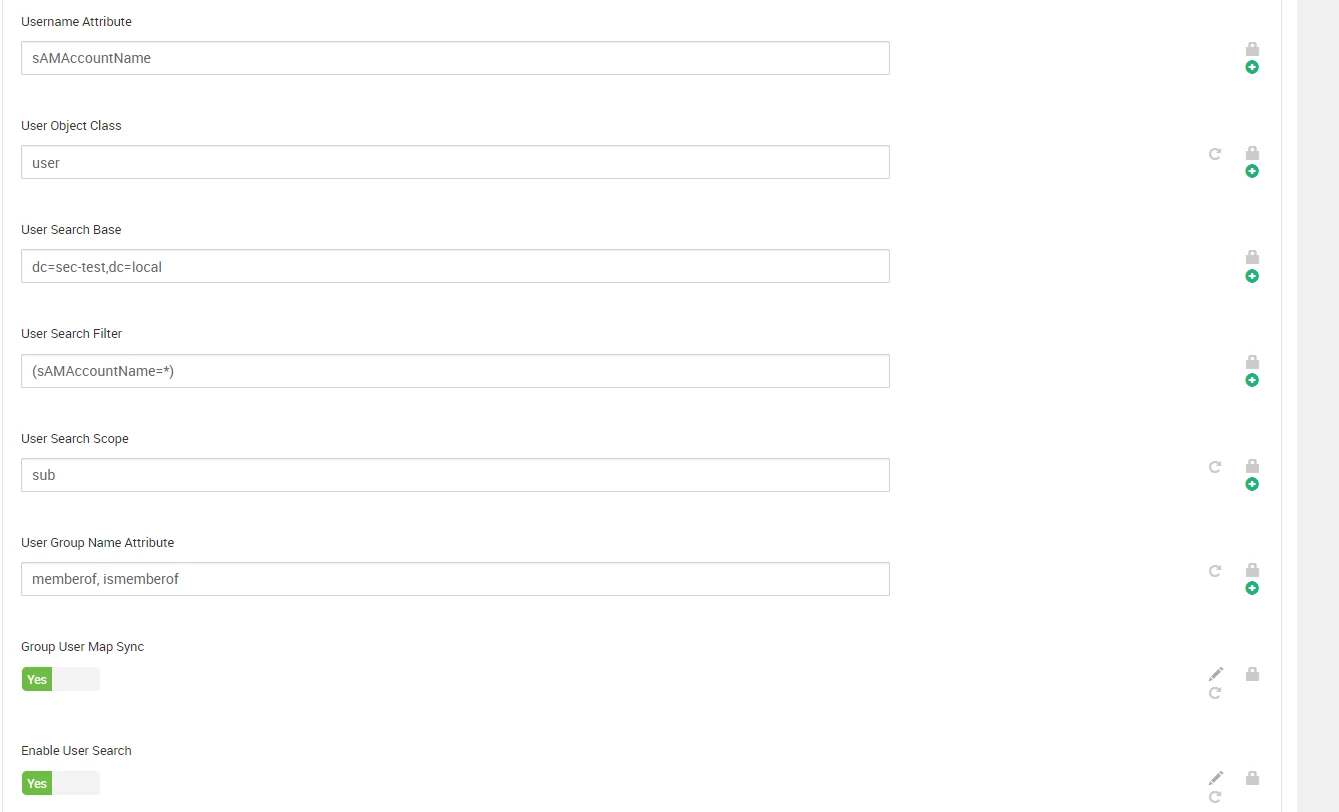
Configured new test instance of Ranger

Settings
bananaman_0-1671614306685.png

bananaman_1-1671614385448.png


Binded user has domain admin rights.

Now synced only 999 users of 1650 existed in AD

What problem can be?

bananaman_2-1671614446488.png


bananaman
bananamanAnswer
Gold ⭐️
December 25, 2022

I solved problem, reason was not in filter

4 replies

arunek95
Gold ⭐️
Gold ⭐️
December 23, 2022

Hi @bananaman , Can you please refer the below docs and enable the user search first and see if it helps. 

https://docs.cloudera.com/cdp-private-cloud-base/7.1.3/security-ranger-authentication-unix-ldap-ad/topics/security-ranger-authentication-ad-integration-usersync.html


Also please try to run ldapsearch to see if it is able to list all the users. 

Translate
bananaman
bananamanAuthor
Gold ⭐️
December 23, 2022

Hi!

As you can see, user search is already enabled, ldapsearch returns 999 results of 1650 in Active Directory....

Translate
Kartik_Agarwal
Platinum ⭐️
Platinum ⭐️
December 24, 2022

@bananaman  This happens when the search filter is not correct. In your case its. Try to change search filter. 


sAMAccountName=*

If this does not help try to add the usersync logs to check further.

Translate
bananaman
bananamanAuthorAnswer
Gold ⭐️
December 25, 2022

I solved problem, reason was not in filter

Translate