Setting up Nifi Registry with Nginx
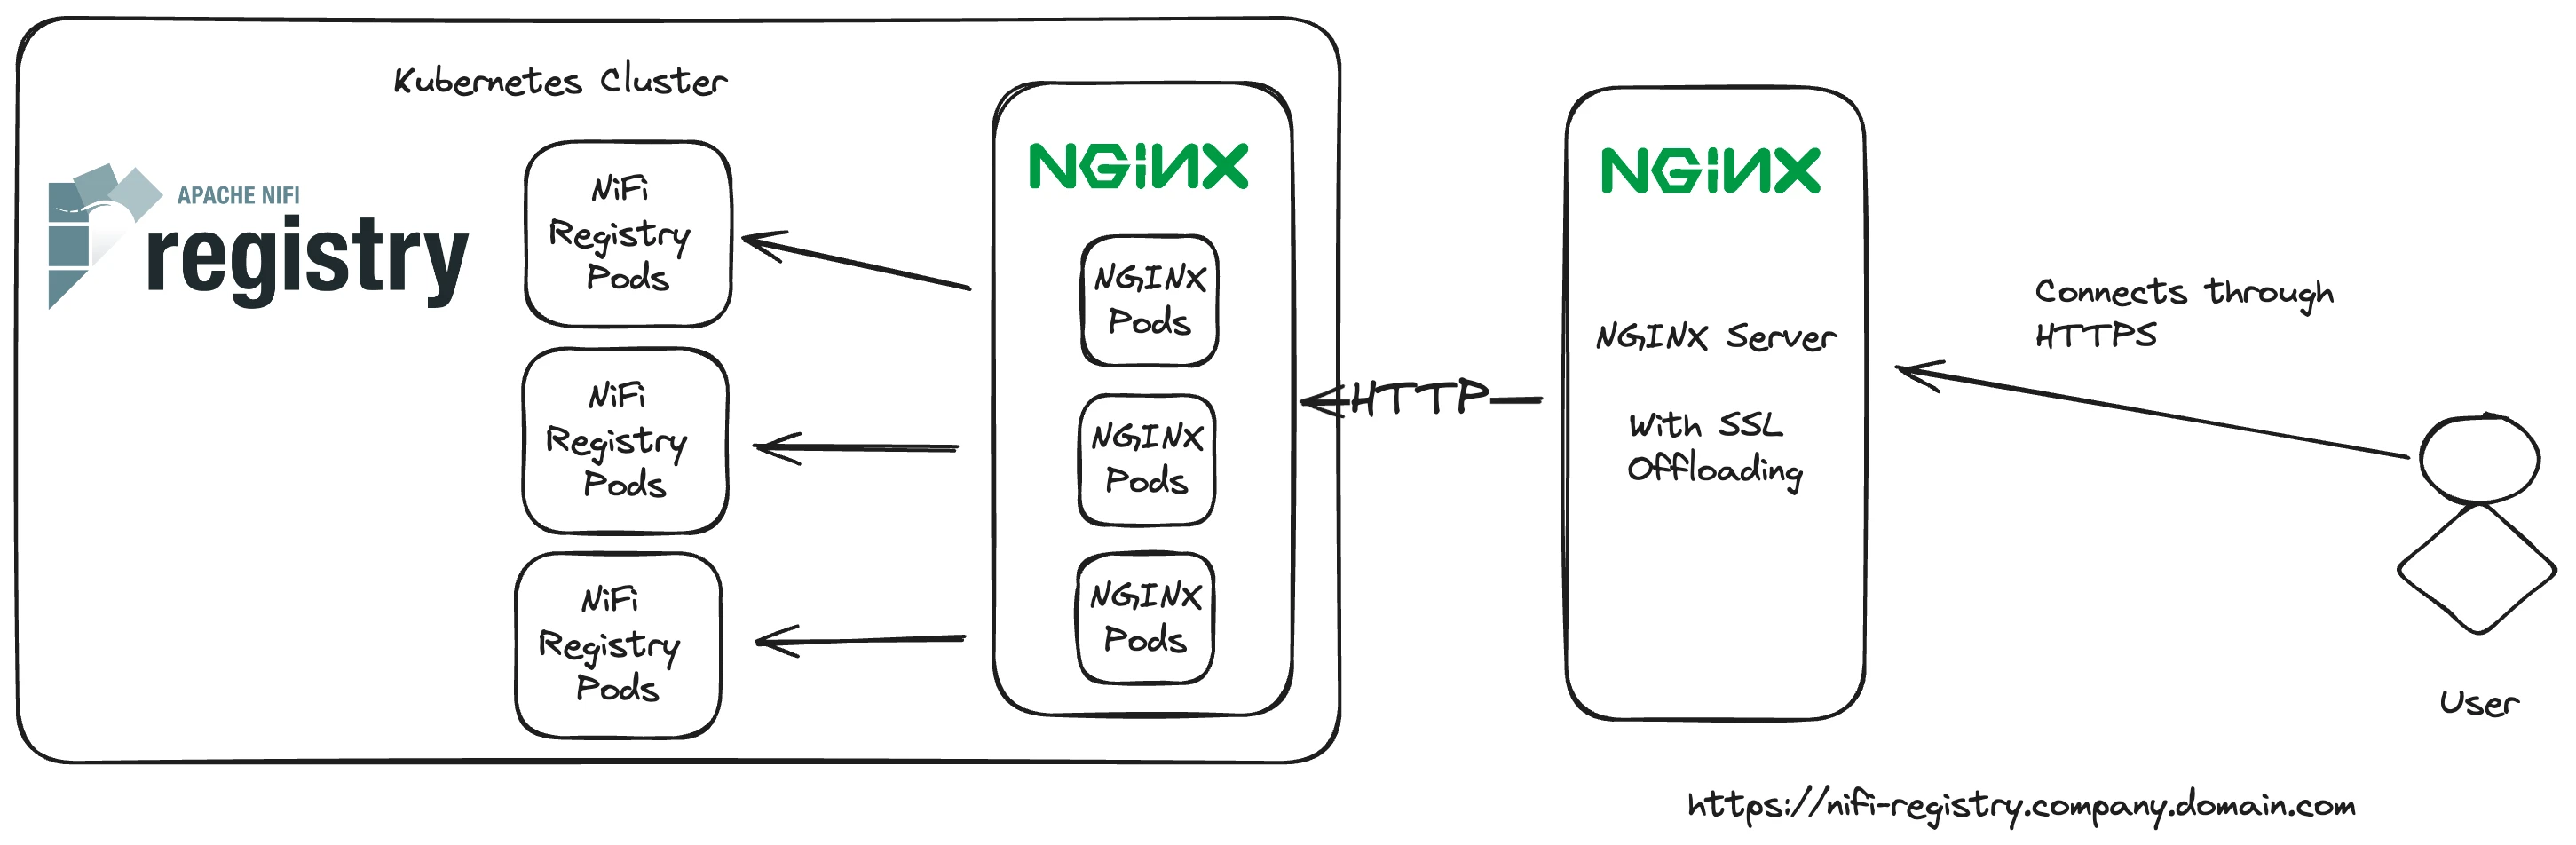
We are working on deploying the NiFi Registry platform on kubernetes, however, we are hitting some issues. I've added a diagram of our deployment to help give some context as well.
Test Case 1: When proxying NiFi registry with settings as unsecure, the proxying works fine. We are able to connect to https://nifi-registry.company.domain.com and view the registry as needed. Note the HTTPS in the URL still - we are using SSL offloading in our nginx's.
Test Case 2: When proxying NiFi registry with settings as secure, we get ERR_TOO_MANY_REDIRECTS. I have attached our nifi-registry.properties file as well. One thing that we found interesting, was that when we tried the below curl request from within the pod we get back a normal response
curl -k --cacert /opt/nifi-registry/nifi-registry-current/tls/cert-manager/ca.crt --key /opt/nifi-registry/nifi-registry-current/tls/cert-manager/tls.key --cert /opt/nifi-registry/nifi-registry-current/tls/cert-manager/tls.crt https://localhost:18443/nifi-registry -vvvvvv -sS -D - The certs are valid as they are generated by cert manager. We are looking for any assistance that you can give, but some of our main questions are as follows:
- In our kubernetes ingress details, should we set the path to just `/` or `/nifi-registry`?
- Is it possible that the NiFi registry is redirecting the client from the HTTPS endpoint a normal HTTP endpoint? We see in the browser network tab that it seems to flip back and forth.
- Is it 100% required to have the authorizers.xml completed in order to get this working?
- Any other ideas of what could be causing this?