@Rupesh_Raghani
NiFI templates are uploaded to the process group selected. Only users who have been granted view and modify on that PG will be able to instantiate those templates on to the NiFi canvas.
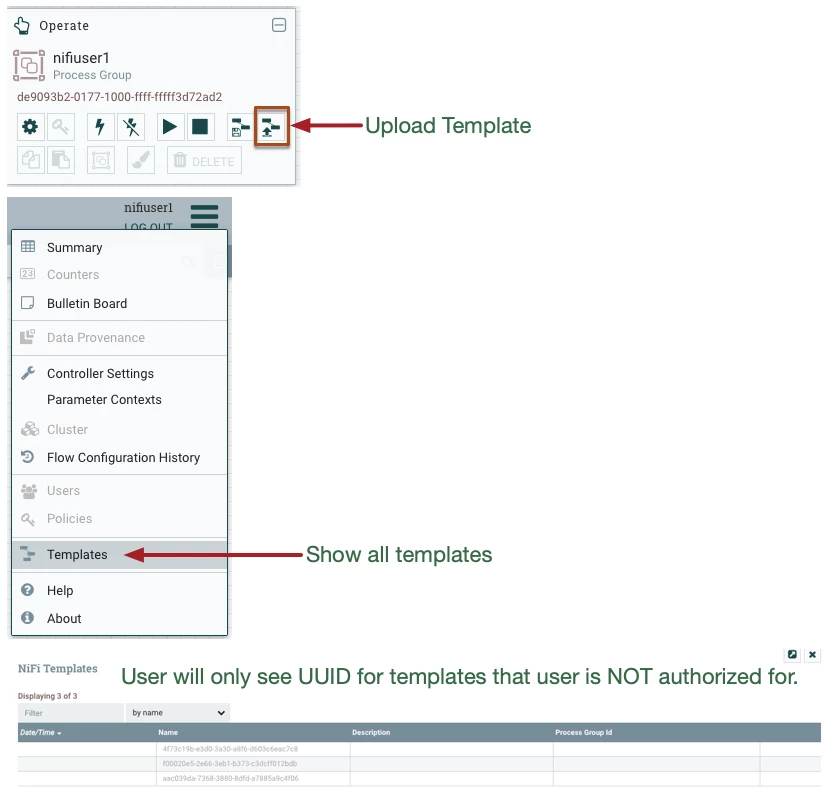
NiFi operates within a single JVM, so there are not separate per user canvases.
User not authorized on a specific NiFi Process Group (PG) will only see a blank representation for that component on the canvas (non-authorized users can not see name, description, configuration details, etc...). Non-authorized users can still see metrics presented on components and queue counts on connections only.
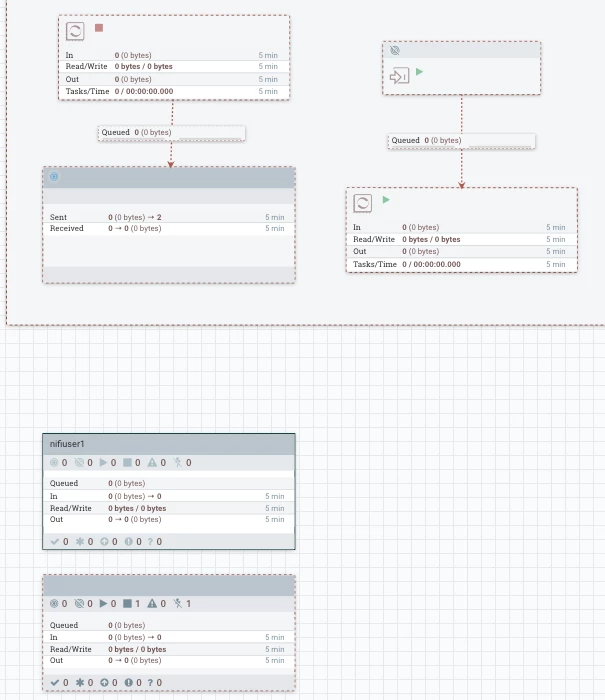
The reason NiFi still renders all components is because everything is executing within a single JVM.
- One users flows can impact another team (Some flow with huge backlog of queued data, high volume, etc can impact resource availability to other teams/users.
- Stats on information bar is representative of entire canvas (all dataflows), so it is still important for all teams/users to be able to identify areas of concern even if is not their dataflows and they have no authorizations allowing them to do anything about it. But they could alert other teams/users.
- Typical use case is team/user 1 has a PG and then team/user 2 has a different authorized PG. If NiFi did not render both PG to both users, nothing prevents users from building flows on top of one another. Then assume we have team/user 3 that is authorized for both above team/users PGs. This becomes unreadable useable by that third user.
If you found this helped with your query, please take a moment to login and click "Accept" on this solution.
Thank you,
Matt




