

Sayed016
Gold ⭐️
March 24, 2022
Solved

Knox authentication with PAM

Hello Team,


I have an issue with setting the Knox authentication with PAM. I have the default login in /etc/pam.d/


$ cat /etc/pam.d/login
#%PAM-1.0
auth [user_unknown=ignore success=ok ignore=ignore default=bad] pam_securetty.so
auth substack system-auth
auth include postlogin
account required pam_nologin.so
account include system-auth
password include system-auth
# pam_selinux.so close should be the first session rule
session required pam_selinux.so close
session required pam_loginuid.so
session optional pam_console.so
# pam_selinux.so open should only be followed by sessions to be executed in the user context
session required pam_selinux.so open
session required pam_namespace.so
session optional pam_keyinit.so force revoke
session include system-auth
session include postlogin
-session optional pam_ck_connector.so


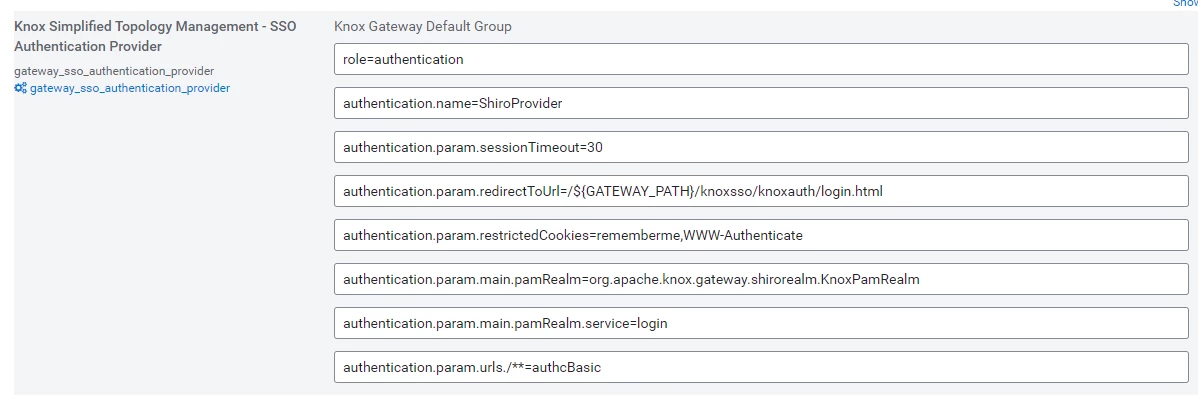
Knox-sso looks as following (the default one)
Sayed016_0-1648116799273.png


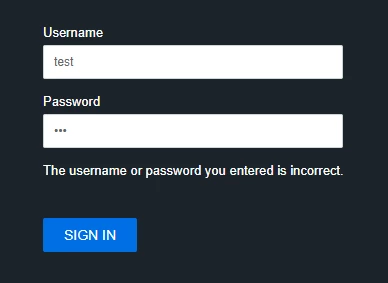
I created a user named - test with a password. I tried to access the Knox Gateway UI but I get the issue.
Sayed016_1-1648116170710.png


The Knox Gateway log says:


(KnoxPamRealm.java:handleAuthFailure(170)) - Shiro unable to login: null


Note: I am using CDP 7.1.6 and I can login to my host (where Knox Gateway is installed) using the test user. Also, there's no Kerberos setup.


Please share if there's something that needs to be adjusted.


Best Regards

Sayed



Scharan
ScharanAnswer
Gold ⭐️
March 24, 2022

@Sayed016 Can you check the permission on /etc/shadow file, make sure it has 444 permission

8 replies

Scharan
Gold ⭐️
ScharanAnswer
Gold ⭐️
March 24, 2022

@Sayed016 Can you check the permission on /etc/shadow file, make sure it has 444 permission

Translate
Sayed016
Sayed016Author
Gold ⭐️
March 24, 2022

Yes, that resolved the issue! I had 000 as my permission. Thank you @Scharan I appreciate the quick reply.


Translate
Sayed016
Sayed016Author
Gold ⭐️
March 24, 2022

@Scharan Can you please give a short explanation as my customer is asking for it as to why shadow file matters in this case i.e. what's the relation with Knox with shadow file? Thank you! 


Translate
Scharan
Gold ⭐️
Gold ⭐️
March 24, 2022

@Sayed016 Not only knox whatever the service may  be the Pam authentication requires Read permission on /etc/shadow file 

Refer to the below doc for more info

https://www.redhat.com/sysadmin/pluggable-authentication-modules-pam

Translate
Sayed016
Sayed016Author
Gold ⭐️
March 24, 2022

@Scharan Thank you! This helps. I appreciate!


Translate
naymar
Silver ⭐️⭐️
September 1, 2022

Resolved my error. Thanks

Translate
S_chinna
Silver ⭐️
March 15, 2024

Hi Sayed,


i Would like to know that how you have created user to access KNOX web UI

Translate
Scharan
Gold ⭐️
Gold ⭐️
March 15, 2024

@S_chinna  To create user follow below steps on knox host

# useradd <Username> (to create a user)
# passwd <Username> (to set the password)
- Set read permission on /etc/shadow  file  for knox user and try to login with the above created credentials

Translate

