

Solved
NiFi Authentication with LDAP
I have installed Apache nifi 1.19.1 and configured the ssl using below command
./tls-toolkit.sh standalone -n 'nifi1,nifi2,nifi3' -B MyPassword -C 'CN=nifiadmin,OU=NIFI' -O -o /opt/nificert
and it was wotking fine after importing the certificate in my browser.
Then configured LDAP like below:-
loginIdentityProviders
<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<loginIdentityProviders>
<provider>
<identifier>ldap-provider</identifier>
<class>org.apache.nifi.ldap.LdapProvider</class>
<property name="Authentication Strategy">SIMPLE</property>
<property name="Manager DN">cn=Myuser,ou=Myuser,dc=Mydomain,dc=com</property>
<property name="Manager Password">Mypassword</property>
<property name="Referral Strategy">FOLLOW</property>
<property name="Connect Timeout">10 secs</property>
<property name="Read Timeout">10 secs</property>
<property name="Url">ldap://x.x.x.x:389</property>
<property name="User Search Base">dc=Mydomain,dc=com</property>
<property name="User Search Filter">(sAMAccountName={0})</property>
<property name="Identity Strategy">USE_USERNAME</property>
<property name="Authentication Expiration">12 hours</property>
</provider>
</loginIdentityProviders>
authorizers
<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<authorizers>
    <userGroupProvider>
        <identifier>file-user-group-provider</identifier>
        <class>org.apache.nifi.authorization.FileUserGroupProvider</class>
        <property name="Users File">./conf/users.xml</property>
        <property name="Legacy Authorized Users File"></property>
        <property name="Initial User Identity 2">CN=nifi1, OU=NIFI</property>
        <property name="Initial User Identity 3">CN=nifi2, OU=NIFI</property>
        <property name="Initial User Identity 4">CN=nifi3, OU=NIFI</property>
        <property name="Initial User Identity 1">cn=Myuser,ou=Myuser,dc=Mydomain,dc=com</property>
    </userGroupProvider>
    <userGroupProvider>
        <identifier>ldap-user-group-provider</identifier>
        <class>org.apache.nifi.ldap.tenants.LdapUserGroupProvider</class>
        <property name="Authentication Strategy">SIMPLE</property>
        <property name="Manager DN">cn=Myuser,ou=Myuser,dc=Mydomain,dc=com</property>
        <property name="Manager Password">Mypassword</property>
        <property name="Referral Strategy">FOLLOW</property>
        <property name="Connect Timeout">10 secs</property>
        <property name="Read Timeout">10 secs</property>
        <property name="Url">ldap://Mydomain:389</property>
        <property name="Page Size"></property>
        <property name="Sync Interval">30 mins</property>
        <property name="Group Membership - Enforce Case Sensitivity">false</property>
        <property name="User Search Base">dc=Mydomain,dc=com</property>
        <property name="User Object Class">person</property>
        <property name="User Search Scope">ONE_LEVEL</property>
        <property name="User Search Filter">(uid=*)</property>
        <property name="User Identity Attribute">cn</property>
        <property name="User Group Name Attribute"></property>
        <property name="User Group Name Attribute - Referenced Group Attribute"></property>
        <property name="Group Search Base"></property>
        <property name="Group Object Class">group</property>
        <property name="Group Search Scope">ONE_LEVEL</property>
        <property name="Group Search Filter"></property>
        <property name="Group Name Attribute"></property>
        <property name="Group Member Attribute"></property>
        <property name="Group Member Attribute - Referenced User Attribute"></property>
    </userGroupProvider>
   <userGroupProvider>
        <identifier>composite-configurable-user-group-provider</identifier>
        <class>org.apache.nifi.authorization.CompositeConfigurableUserGroupProvider</class>
        <property name="Configurable User Group Provider">file-user-group-provider</property>
        <property name="User Group Provider 1">ldap-user-group-provider</property>
    </userGroupProvider>
    <accessPolicyProvider>
        <identifier>file-access-policy-provider</identifier>
        <class>org.apache.nifi.authorization.FileAccessPolicyProvider</class>
        <property name="User Group Provider">composite-configurable-user-group-provider</property>
        <property name="Authorizations File">./conf/authorizations.xml</property>
        <property name="Initial Admin Identity">cn=Myuser,ou=Myou,dc=Mydomain,dc=com</property>
        <property name="Legacy Authorized Users File"></property>
        <property name="Node Identity 1">CN=nifi1, OU=NIFI</property>
        <property name="Node Identity 2">CN=nifi2, OU=NIFI</property>
        <property name="Node Identity 3">CN=nifi3, OU=NIFI</property>
        <property name="Node Group"></property>
    </accessPolicyProvider>
    <authorizer>
        <identifier>managed-authorizer</identifier>
        <class>org.apache.nifi.authorization.StandardManagedAuthorizer</class>
        <property name="Access Policy Provider">file-access-policy-provider</property>
    </authorizer>
</authorizers>
I also changed nifi.properities
but still getting below error
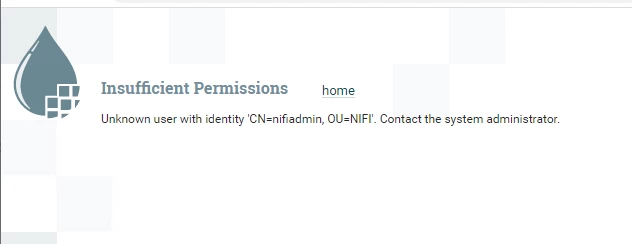
Any help will be high appreciated


