
Solved
Unable to add users in Apache NiFi Registry
Hello, everyone.
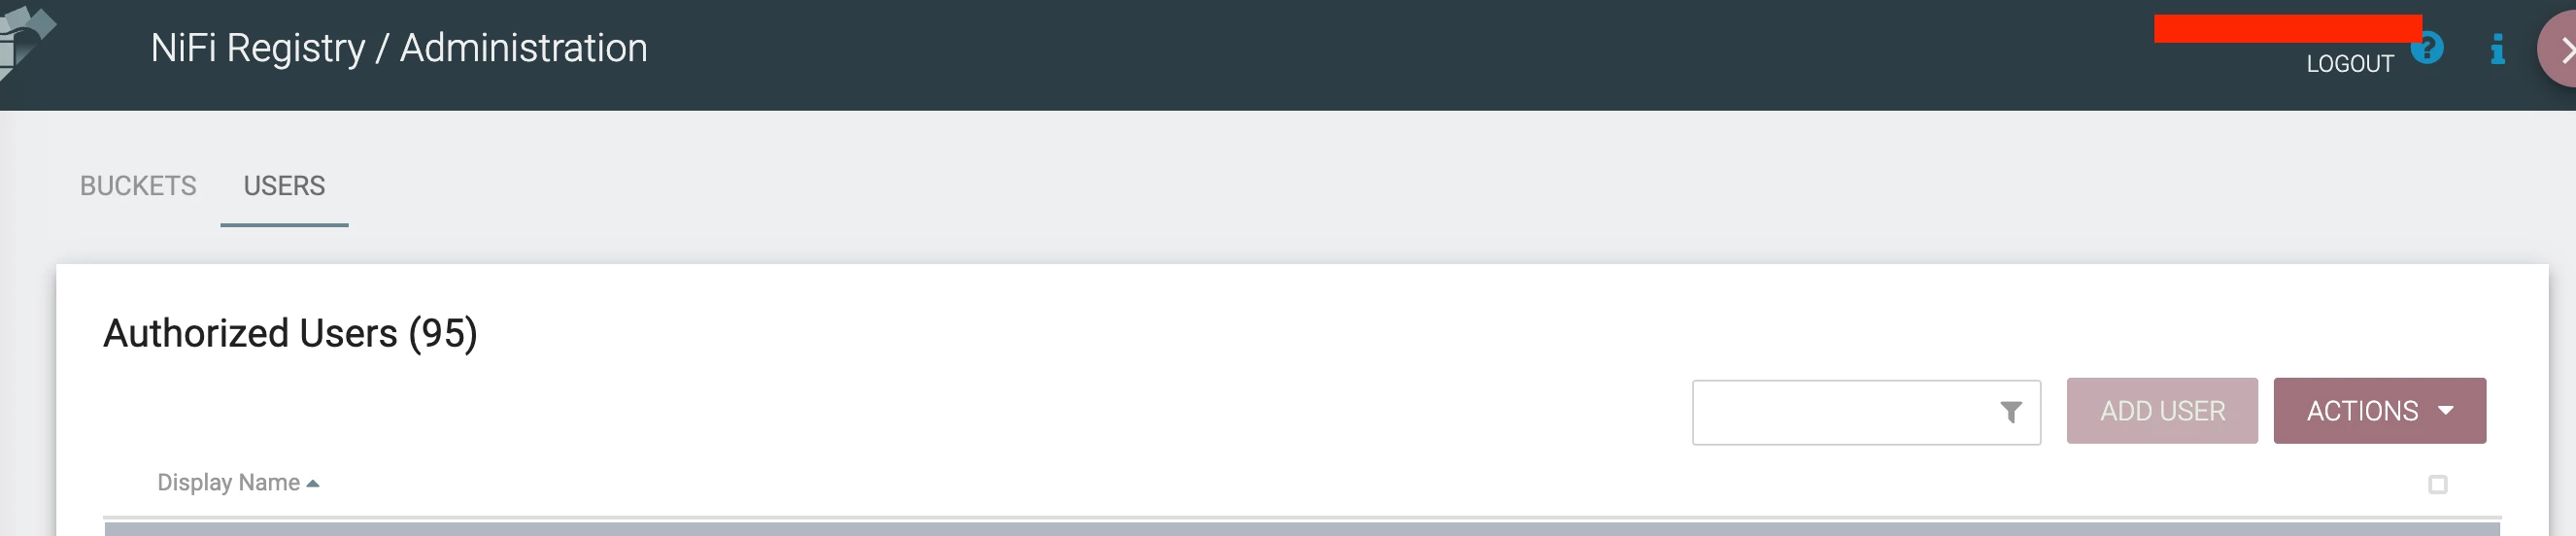
I have an issue with NiFi Registry 1.20 -- UI button "Add user" is inactive with Initial Admins account.
But, if I check the user permissions, it looks good enough:
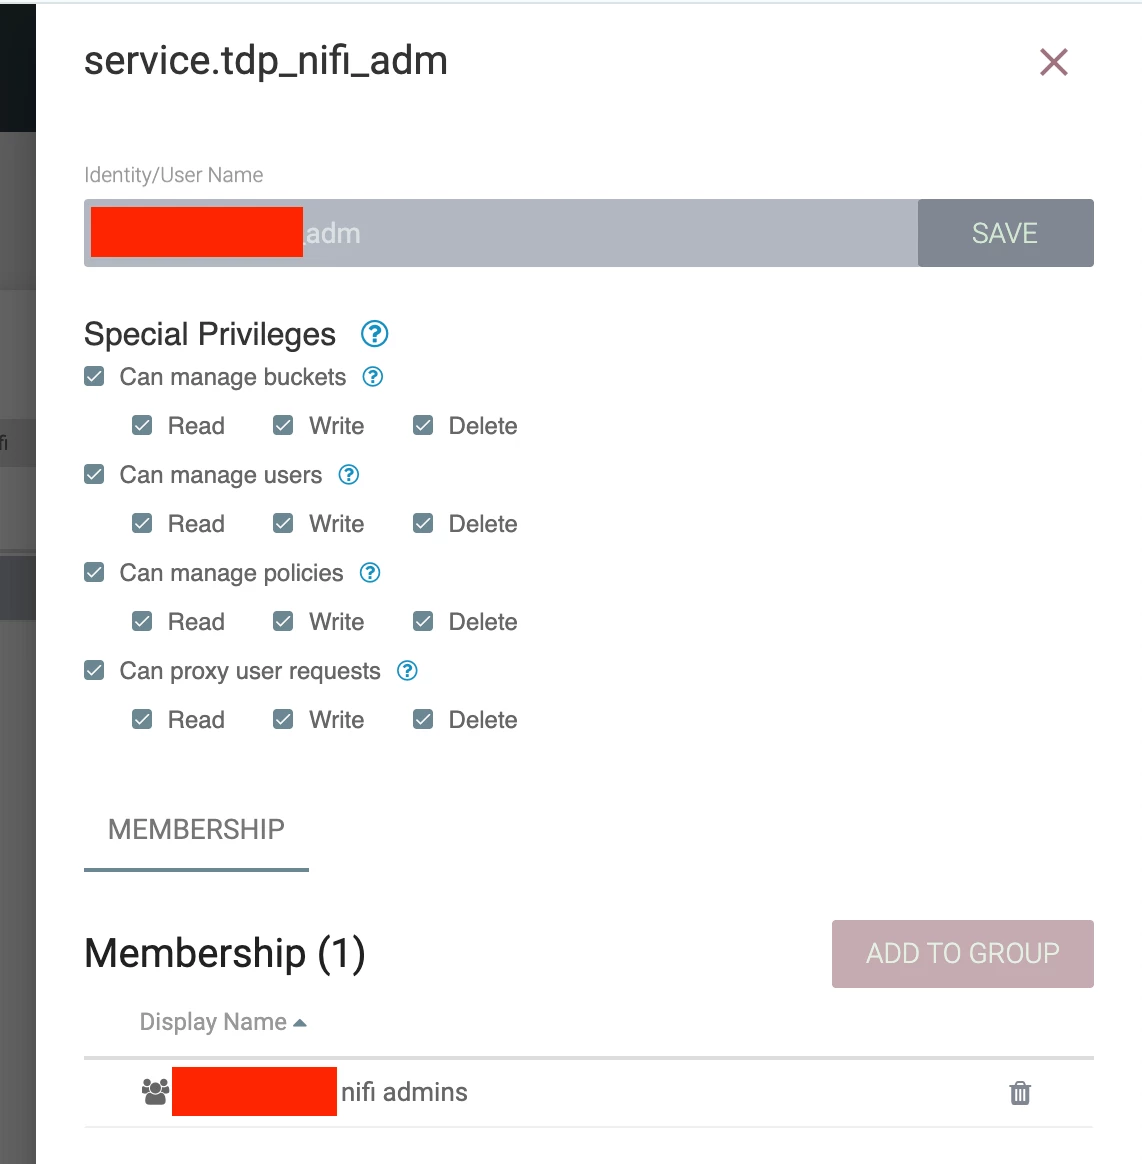
The Initial Admin user is LDAP user and also member of "nifi admins" LDAP group.
My authorizers.xml file:
<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<authorizers>
<userGroupProvider>
        <identifier>ldap-user-group-provider-1</identifier>
        <class>org.apache.nifi.registry.security.ldap.tenants.LdapUserGroupProvider</class>
        <property name="Authentication Strategy">LDAPS</property>

        <property name="Manager DN">user</property>
        <property name="Manager Password">password</property>
        <property name="TLS - Keystore">./conf/keystore.jks</property>
        <property name="TLS - Keystore Password">pass</property>
        <property name="TLS - Keystore Type">JKS</property>
        <property name="TLS - Truststore">./conf/truststore.jks</property>
        <property name="TLS - Truststore Password">pass</property>
        <property name="TLS - Truststore Type">JKS</property>
        <property name="TLS - Client Auth">None</property>
        <property name="TLS - Protocol">TLSv1.2</property>
        <property name="TLS - Shutdown Gracefully"></property>

        <property name="Referral Strategy">FOLLOW</property>
        <property name="Connect Timeout">10 secs</property>
        <property name="Read Timeout">60 secs</property>

        <property name="Url">ldaps://ldap.company.com</property>
        <property name="Page Size">500</property>
        <property name="Sync Interval">5 mins</property>
        <property name="Group Membership - Enforce Case Sensitivity">false</property>

        <property name="User Search Base">ou</property>
        <property name="User Object Class">user</property>
        <property name="User Search Scope">SUBTREE</property>
        <property name="User Search Filter">some filter</property>
        <property name="User Identity Attribute">sAMAccountName</property>
        <property name="User Group Name Attribute"></property>
        <property name="User Group Name Attribute - Referenced Group Attribute"></property>

        <property name="Group Search Base">ou</property>
        <property name="Group Object Class">group</property>
        <property name="Group Search Scope">SUBTREE</property>
        <property name="Group Search Filter">some search filter</property>
        <property name="Group Name Attribute">cn</property>
        <property name="Group Member Attribute">member</property>
        <property name="Group Member Attribute - Referenced User Attribute">distinguishedName</property>
    </userGroupProvider>

    <userGroupProvider>
        <identifier>ldap-user-group-provider-2</identifier>
        ....
    </userGroupProvider>

    <userGroupProvider>
        <identifier>ldap-user-group-provider-3</identifier>
        ....
    </userGroupProvider>

    <userGroupProvider>
        <identifier>ldap-user-group-provider-4</identifier>
        ....
    </userGroupProvider>

    <userGroupProvider>
        <identifier>file-user-group-provider</identifier>
        <class>org.apache.nifi.registry.security.authorization.file.FileUserGroupProvider</class>
        <property name="Users File">/opt/nifi-registry/nifi-registry-current/conf/authorizations/users.xml</property>
        <property name="Initial User Identity 1">cn=some_init_user_for_nifi_01, ou=nifi</property>
        <property name="Initial User Identity 2">cn=some_init_user_for_nifi_02, ou=nifi</property>
        <property name="Initial User Identity 3">cn=some_init_user_for_nifi_03, ou=nifi</property>
    </userGroupProvider>

    <userGroupProvider>
        <identifier>composite-configurable-user-group-provider</identifier>
        <class>org.apache.nifi.registry.security.authorization.CompositeUserGroupProvider</class>
        <property name="User Group Provider 0">file-user-group-provider</property>
        <property name="User Group Provider 1">ldap-user-group-provider-1</property>
        <property name="User Group Provider 2">ldap-user-group-provider-2</property>
        <property name="User Group Provider 3">ldap-user-group-provider-3</property>
        <property name="User Group Provider 4">ldap-user-group-provider-4</property>
    </userGroupProvider>

    <accessPolicyProvider>
        <identifier>file-access-policy-provider</identifier>
        <class>org.apache.nifi.registry.security.authorization.file.FileAccessPolicyProvider</class>
        <property name="User Group Provider">composite-configurable-user-group-provider</property>
        <property name="Authorizations File">/opt/nifi-registry/nifi-registry-current/conf/authorizations/authorizations.xml</property>
        <property name="Initial Admin Identity">init_admin_name</property>
    </accessPolicyProvider>

    <authorizer>
        <identifier>managed-authorizer</identifier>
        <class>org.apache.nifi.registry.security.authorization.StandardManagedAuthorizer</class>
        <property name="Access Policy Provider">file-access-policy-provider</property>
    </authorizer>
</authorizers>
Could you guess please what is wrong?


