
Authorization configured for nifi resources in ranger not working properly
Currently I have configured apache NiFi with Ranger as per discussed in this thread. Ranger NiFi plugin is able to pull resources from ranger and auto suggest in ranger nifi service definition UI. But I don't think the authorizations works properly.
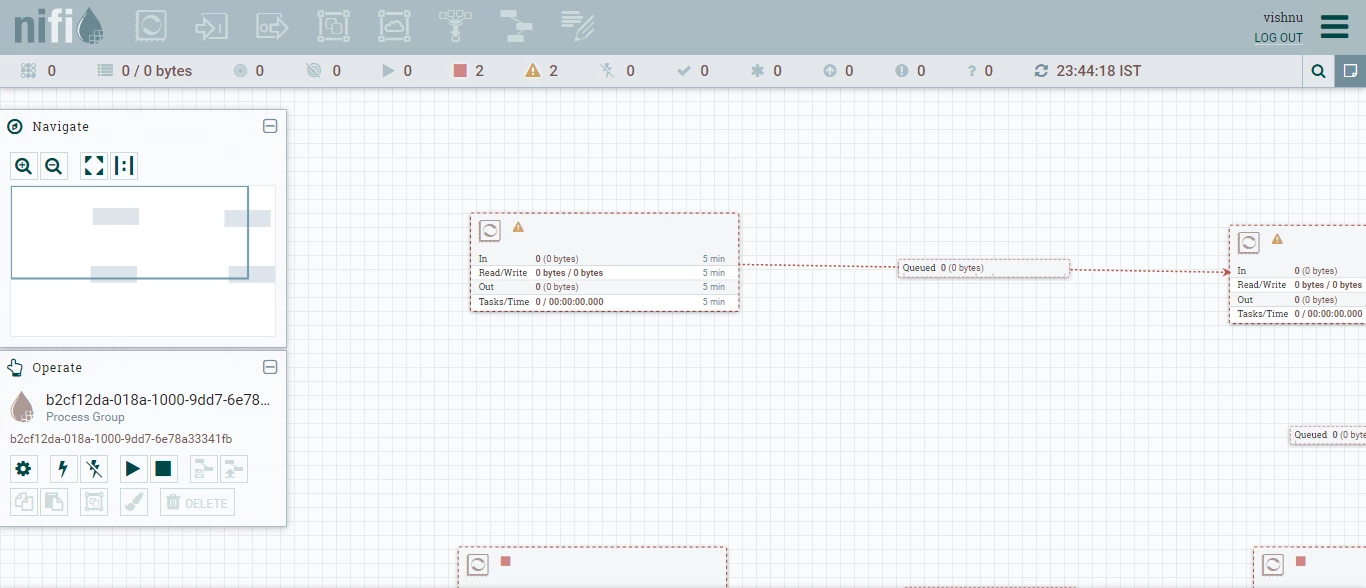
Only the /flow resource specifier has an impact. When I remove that specifier user is not able to view the screen and when I add it back the user is logging back into the Nifi UI. Rest of the resources including processors , ports etc. seems to be unclickable or accessible no matter any of the resource specifier I provide in ranger. I even tried the wild card * but still doesn't seems to work. The UI looks as below.
The Ranger Authorizers file is shown below
    <userGroupProvider>
        <identifier>file-user-group-provider</identifier>
        <class>org.apache.nifi.authorization.FileUserGroupProvider</class>
        <property name="Users File">./conf/users.xml</property>
        <property name="Legacy Authorized Users File"></property>
        <property name="Initial User Identity 1"></property>
    </userGroupProvider>

    <accessPolicyProvider>
        <identifier>file-access-policy-provider</identifier>
        <class>org.apache.nifi.authorization.FileAccessPolicyProvider</class>
        <property name="User Group Provider">file-user-group-provider</property>
        <property name="Authorizations File">./conf/authorizations.xml</property>
        <property name="Initial Admin Identity"></property>
        <property name="Legacy Authorized Users File"></property>
        <property name="Node Identity 1"></property>
        <property name="Node Group"></property>
    </accessPolicyProvider>

  <authorizer>
     <identifier>ranger-provider</identifier>
     <class>org.apache.nifi.ranger.authorization.RangerNiFiAuthorizer</class>
     <property name="Ranger Audit Config Path">./conf/ranger-nifi-audit.xml</property>
     <property name="Ranger Security Config Path">./conf/ranger-nifi-security.xml</property>
     <property name="Ranger Service Type">nifi</property>
     <property name="Ranger Application Id">nifi</property>
     <property name="Ranger Admin Identity">CN=localhost, OU=NIFI</property>
     <property name="Ranger Kerberos Enabled">false</property>
   </authorizer>
The initial admin is specified for resource access through user present in the certificate.


