Our Community is getting an upgrade! To get everything ready for the relaunch, we’ll be placing the site in read-only mode starting September 21st.
We really appreciate your understanding while we get things set up behind the scenes. Catch up on all the exciting details about the move here.
Need help or have questions? Drop us a line at [email protected]
Created on 06-19-2016 08:15 PM - edited 08-17-2019 11:49 AM
Note - For this tutorial I assume that you already have HDP cluster kerberized. If you want to configure automated kerberos then please refer to https://community.hortonworks.com/articles/29203/automated-kerberos-installation-and-configuration.h....
.
.
.
1 Login to kadmin and create principal for Ambari Server
Note - Please replace your REALM in REALM.COM
addprinc -randkey [email protected]
.
2 Extract principal created in above step to keytab filexst -k ambari.server.keytab [email protected]
.
3 Above command should generate keytab file in current working directory, copy keytab file to /etc/security/keytabs/ locationcp ambari.server.keytab /etc/security/keytabs/ambari.server.keytab
Note - Please make sure that, user running ambari server daemon should have read access to ambari.server.keytab
.
4 Stop Ambari server daemon and setup security using below command.service ambari-server stop ambari-server setup-security
.
5 Select 3 for Setup Ambari kerberos JAAS configuration. Enter the Kerberos principal name for the Ambari Server you set up in step 1.1. Enter the path to the keytab for the Ambari principal. Restart Ambari Server.ambari-server restart
.
6. Add below properties in yarn-site.xml using Ambari UI.yarn.timeline-service.http-authentication.proxyuser.ambari-server.hosts=* yarn.timeline-service.http-authentication.proxyuser.ambari-server.users=* yarn.timeline-service.http-authentication.proxyuser.ambari-server.groups=*
.
7. Add below properties in core-site.xmlhadoop.proxyuser.ambari-server.hosts=* hadoop.proxyuser.ambari-server.groups=* hadoop.proxyuser.admin.hosts=* hadoop.proxyuser.admin.groups=*
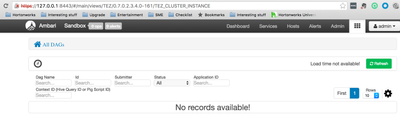
Your TEZ view should be accessible now!
.
.
Happy Hadooping!! 🙂
Created on 06-20-2016 11:59 PM
In order to work with the Tez view in a Kerberized environment, follow the instructions given at the following link:
Created on 06-21-2016 12:17 AM
In order to work with the Tez view in a Kerberized environment, follow these instructions
Created on 08-03-2016 06:55 PM
I've all these properties in place. Tez view is working fine, however it's not showing any jobs after we implemented kerberos.