@SAMSAL
Sounds like you are very close...
The 403 has nothing to do with authentication, but rather authorization.
This eludes to the fact that the client was able to be properly trusted through the mutual TLS handshake, but when that resulting client string was checked against the endpoint policy being checked it was not present, thus resulting in a 403 response.
The DN is the DistinquishedName for your certificate. You can use the below command to get the verbose details on the certs added to a keystore:
keytool -v -list -keystore <keystore.jks or truststore.jks>
You will see that each certificate has either type "PrivateKeyEntry" or "TrustedCertEntry"
For each certificate you will see an "Owner" and an "Issuer"
For each of those it will show the complete DN which would look something like:
CN=<some string>, OU=<some string>, DC=<some string>
There are numerous parts that can be part (CN, OU, O, ST, DC, etc.) of a DN and various lengths
The "Owner" DN for the PrivateKeyEntry is what is used as the client/user authenticated string after the successful mutual TLS handshake. The nifi.properties file has optional ideNtity.mapping properties that can be configured to trim and manipulated these identity strings (for example pulling our on the string from the CN).
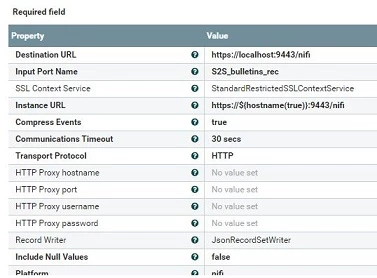
With nifi.remote.input.secure= set to false, FlowFiles send over S2S will not be over a TLS encrypted connection. The fact that you say it works when you have this set to false and you can still successfully obtain S2S details from the configured https:// secured NiFi Destination URL tells me that authentication is correct for "Retrieve site-to-site details" NiFi policy. That only leaves having incorrect policy setup for your remote input port.
You should open a command prompt on each node and "tail -F /<path to>/nifi-user.log". Then enable your controller services and check the logs being tailed for the authorization exception. It should clearly show you the "string" being checked against the "receive data via site-to-site" endpoint which in the log would look like "/data-transfer/input-ports/<uuid of remote input port>". Also remember that you are NOT authorizing your user to any of these S2S policies, but rather the DN or identity mapped DN string.
Really hope this helps you get fully secured here.
Matt