hbashir
Silver ⭐️⭐️⭐️
January 3, 2019
Solved

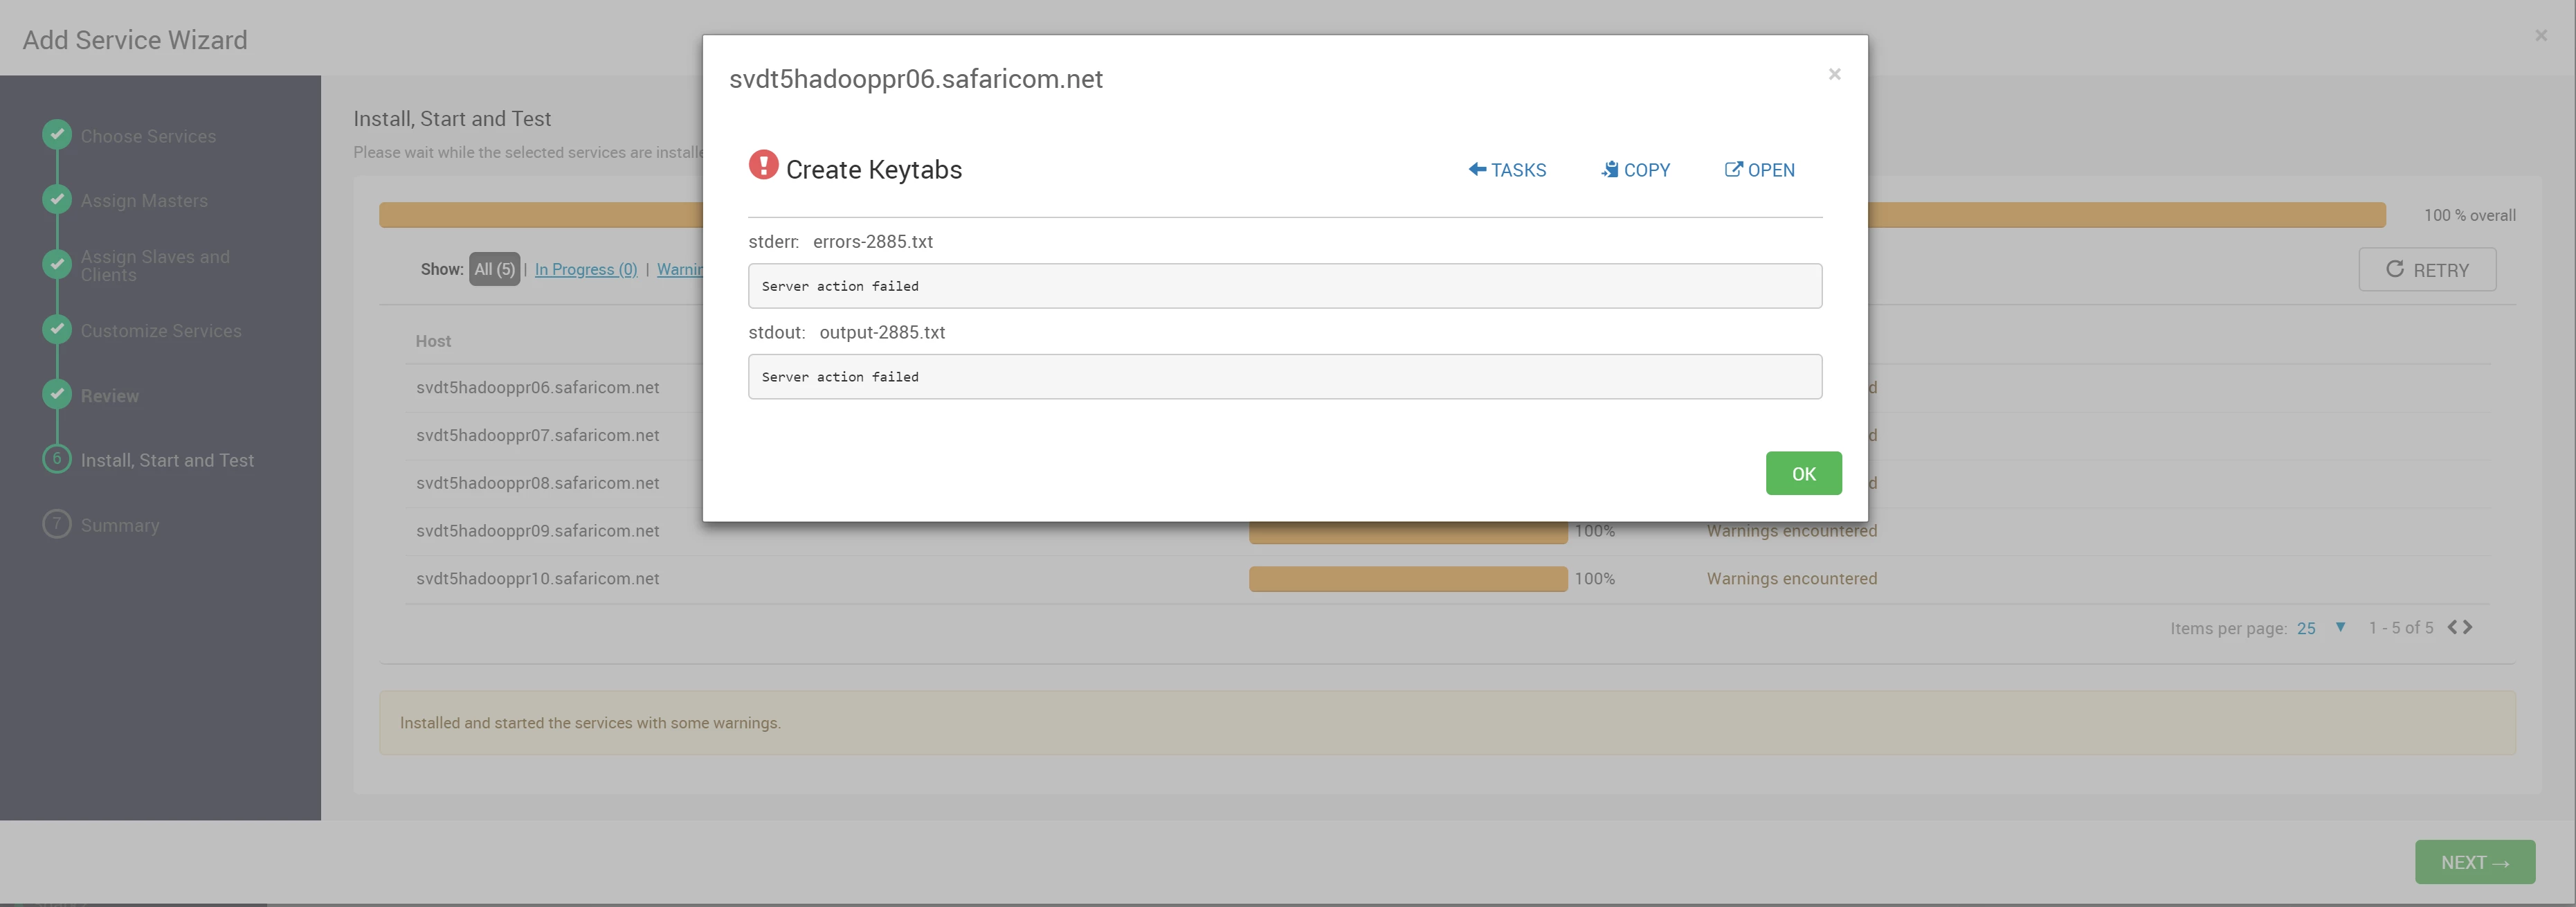
Ambari Fails to create Keytabs when Installing new services or when trying to regenerate keytabs of existing services

I am getting a server action failed error when ambari tries to create keytabs. I have no idea what is causing this error. I am using KDC admin to install the service. Please help. @Geoffrey Shelton Okot

96567-keytab-error.png

Shelton
SheltonAnswer
Gold ⭐️⭐️⭐️
January 16, 2019

@huzaira bashir

There seems to be a mismatch between the Active Directory encryption type and the MIT encryption types can you align the 2 supported_enctypes to be the same.

Windows supports the below encryption types depending on the Windows version which are weak encryption

DES_CBC_CRC
DES_CBC_MD5
RC4_HMAC_MD5
AES128_HMAC_SHA1
AES256_HMAC_SHA1

In your kdc.conf you have stronger encryption types you validate the AD encryption types? Else try to comment out the kdc.conf encryptions see below

# supported_enctypes = aes256-cts:normal aes128-cts:normal des3-hmac-sha1:normal arcfour-hmac:normal camellia256-cts:normal camellia128-cts:normal des-hmac-sha1:normal des-cbc-md5:normal des-cbc-crc:normal

and see whether the error persists?

27 replies

mRabramS
Silver ⭐️⭐️⭐️
January 15, 2019

@Geoffrey Shelton Okot @huzaira bashir

Did you manage to solve this yet?

What was the problem?

Translate
Shelton
Gold ⭐️⭐️⭐️
January 15, 2019

@Javert Kirilov

Have you encountered a Kerberos issue? Is it similar to the thread opened by Bashir? It's usually good to open a new thread as this one isn't being actively viewed.
I will be happy to help you if you attached some logs ,screenshot and some error logs

Translate
mRabramS
Silver ⭐️⭐️⭐️
January 15, 2019

Thank you, I had this exact issue with same errors and nothing in the comment discussion helped. However, after several ambari-server restarts and dumb retries of the "Kerberos wizard" with similar settings magically resolved this. I'm not sure at all what was the problem..

Translate
hbashir
hbashirAuthor
Silver ⭐️⭐️⭐️
January 16, 2019

@Robert Levas @Geoffrey Shelton Okot when I used debug mode I get an additional line which might point to an encryption issue? please see attached pic

97607-debug-error-message.png

Translate
rlevas
Gold ⭐️
January 16, 2019

Interesting.... Actually I am not sure why `UNKNOWN:normal` is in there. Did you edit the encryption types in the configure Kerberos page, under Advanced kerberos-env? It should be `aes des3-cbc-sha1 rc4 des-cbc-md5`. Does your have a different value?

Translate
Shelton
Gold ⭐️⭐️⭐️
January 16, 2019

@huzaira bashir

Can you share your krb5 and kdc conf files for analysis?


Translate
hbashir
hbashirAuthor
Silver ⭐️⭐️⭐️
January 16, 2019
@Geoffrey Shelton Okot

Find attached the 2 files

Translate
rlevas
Gold ⭐️
January 16, 2019

One thing to note is that Ambari appears to not be managing the krb5.conf file. This is fine, but Hadoop does not support the KEYRING cache type. You need to change

default_ccache_name = KEYRING:persistent:%{uid}

to

default_ccache_name = /tmp/krb5cc_%{uid}

Translate
Shelton
SheltonAnswer
Gold ⭐️⭐️⭐️
January 16, 2019

@huzaira bashir

There seems to be a mismatch between the Active Directory encryption type and the MIT encryption types can you align the 2 supported_enctypes to be the same.

Windows supports the below encryption types depending on the Windows version which are weak encryption

DES_CBC_CRC
DES_CBC_MD5
RC4_HMAC_MD5
AES128_HMAC_SHA1
AES256_HMAC_SHA1

In your kdc.conf you have stronger encryption types you validate the AD encryption types? Else try to comment out the kdc.conf encryptions see below

# supported_enctypes = aes256-cts:normal aes128-cts:normal des3-hmac-sha1:normal arcfour-hmac:normal camellia256-cts:normal camellia128-cts:normal des-hmac-sha1:normal des-cbc-md5:normal des-cbc-crc:normal

and see whether the error persists?

Translate
mRabramS
Silver ⭐️⭐️⭐️
January 16, 2019

This is to the point! I got the same error when tried changing the default Ambari suggested enctypes to my custom ones. The custom ones work fine though with MIT KDC, but apparantly not with Ambari.

Translate