Our Community is getting an upgrade! To get everything ready for the relaunch, we’ll be placing the site in read-only mode starting September 21st.
We really appreciate your understanding while we get things set up behind the scenes. Catch up on all the exciting details about the move here.
Need help or have questions? Drop us a line at [email protected]
Created 04-25-2022 02:59 AM
I'm having difficulty with this processor and making sure I get all the security stuff correct.
I've got no problem with everything downstream, but when it comes to Keystore/Truststore stuff I'm like a potato in a forgotten cellar.
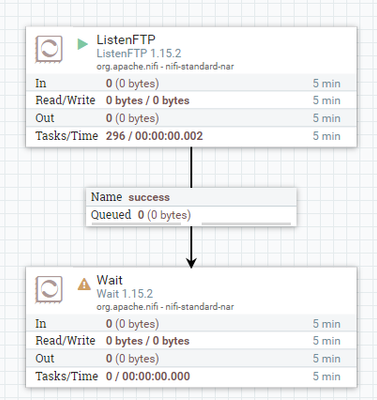
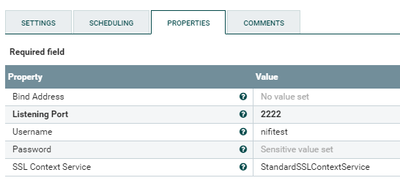
For now, just to test, I have this (nifi 1.15.3):
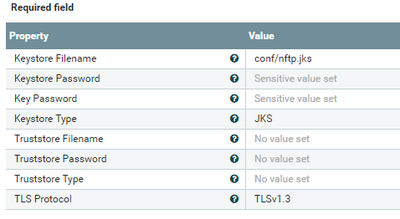
And the SSL Context:
Where my jks was generated using (with testing values)
keytool -genkey -alias nifi-ftps -keyalg RSA -keypass MyKeyPass312 -storepass MyStorePass312 -keystore nftp.jks
When I log on with Filezilla it gets to this point:
Status: Connecting to my.server.ip...
Status: Using username "nifitest".
Status: Access denied
Error: Authentication failed.
Error: Critical error: Could not connect to server
Which I assume means the ports etc are all good and it can connect to the Processor - but I'm missing something in my SSL settings. I have tried changing FileZilla to use a key file but it only uses PPK or PEM files.
This is my java version:
sudo java -version
openjdk version "1.8.0_312"
OpenJDK Runtime Environment (build 1.8.0_312-8u312-b07-0ubuntu1~20.04-b07)
OpenJDK 64-Bit Server VM (build 25.312-b07, mixed mode)
Created 04-25-2022 05:02 AM
Have you tested ListenFTP without setting SSLContextService? just to make sure supplied username and password is correct?
Created 04-25-2022 06:07 AM
@ckumar yes I have - the username and passwords are correct.
Created 04-26-2022 06:06 AM
@Tokolosk I would recommend that you provide java's cacerts as the keystore/truststore with the default password (changeit). This will work for most public certs. If you have a custom cert at the SFTP end you will need to import that cert and create your own keystore/truststore. I always try cacerts first.