
Our Community is getting an upgrade! To get everything ready for the relaunch, we’ll be placing the site in read-only mode starting September 21st.
We really appreciate your understanding while we get things set up behind the scenes. Catch up on all the exciting details about the move here.
Need help or have questions? Drop us a line at [email protected]

Support Questions
 Hi, I'm CLEO! Something exciting is coming to the Community. Stay Tuned!
- Cloudera Community
- Support
- Support Questions
- Re: Not able to update ParameterContent using Nifi...
- Subscribe to RSS Feed
- Mark Question as New
- Mark Question as Read
- Float this Question for Current User
- Bookmark
- Subscribe
- Mute
- Printer Friendly Page
- Subscribe to RSS Feed
- Mark Question as New
- Mark Question as Read
- Float this Question for Current User
- Bookmark
- Subscribe
- Mute
- Printer Friendly Page
Not able to update ParameterContent using Nifi REST API
- Labels:
-
Apache NiFi

Created on 03-11-2024 10:22 PM - edited 03-12-2024 12:22 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hello All,
I am using Nifi 2.0
I want to update existing Parameter Context using Nifi API. For that , following API is used
Where "2ddc0cea-018e-1000-3852-3611d730f705" is the Id of parameter context.
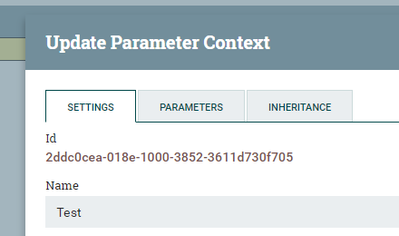
Issue :
I tried to update the ParameterContext using
but its throwing 403 error .
I updated the Request with token (Bearer) but still getting the same error.
Any Pointers..??
Thanks,
Riyaz
Created 03-18-2024 09:51 PM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I am able to solve the problem
Access token Rest API generates two token (check under cookies) - Secure-Request-Token and other is Secure-Authorization-Bearer token.
While calling any of the other API (like creating Parameter Context or updating Parameter context) - in Headers provide one more header "Request-Token" with the value of _secure-Request-Token (From cookies).


Created 03-12-2024 02:32 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@mohdriyaz, Welcome to our community! To help you get the best possible answer, I have tagged in our NiFi experts @cotopaul @SAMSAL @TimothySpann who may be able to assist you further.
Please feel free to provide any additional information or details about your query, and we hope that you will find a satisfactory solution to your question.
Regards,
Vidya Sargur,Community Manager
Was your question answered? Make sure to mark the answer as the accepted solution.
If you find a reply useful, say thanks by clicking on the thumbs up button.
Learn more about the Cloudera Community:

Created 03-12-2024 05:52 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
403 : Client is not authorized to make this request.
This means you are Authenticated and since you have a valid token but you are not authorized to do this action.
to double-check if your user is Authorized, check if you can do the same action directly from NiFi UI ?
Thank you
Created 03-12-2024 10:55 PM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Yes , i am able to do the changes via Nifi UI.
Note :
I have created the user user using following command :
nifi.cmd set-single-user-credentials username password
Created 03-14-2024 07:25 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I would further interested check nifi-user.log to see the forbidden events when you see 403 error
Created 03-18-2024 09:51 PM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I am able to solve the problem
Access token Rest API generates two token (check under cookies) - Secure-Request-Token and other is Secure-Authorization-Bearer token.
While calling any of the other API (like creating Parameter Context or updating Parameter context) - in Headers provide one more header "Request-Token" with the value of _secure-Request-Token (From cookies).


