Hi @mr_jahurley ,
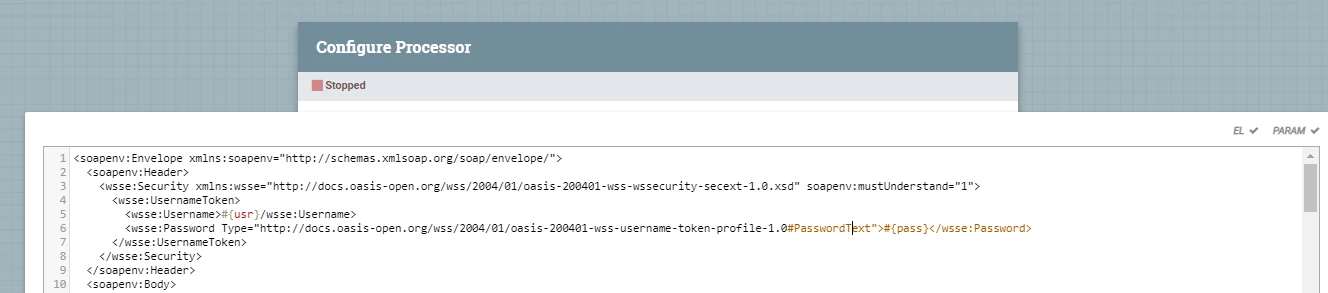
NiFi does not allow the use of sensitive parameters in non-sensitive context to avoid leaking of sensitive information into other parts of your flow, including flowfile contents. If this was possible, you could, for example, inject a sensitive value into a flowfile and anyone with access to a flowfile would be able to see the sensitive values, which would be otherwise encrypted in NiFi.
If that's really what you want/need, I can only see two available solutions:
- Create a non-sensitive property to store the password, and you would be able to use it in the ReplaceText processor. This is less secure, but no less secure than having the password in a flowfile content. So, I guess, to do what you want to do, this could be a viable alternative.
- Alternatively, you can create your own processor with a sensitive password property where you would be able to use the sensitive parameter. This processor could then take the sensitive value and modify the flowfile content as needed. Notice, though, that after being processed by this processor, the flowfile would contain the password in plain text, so anyone inspecting the flowfile after that would be able to see that. In that sense, this is still somewhat insecure since that password could be leaked. But again, it may be a necessary evil for what you need to implement.
Hope this helps,
André
--
Was your question answered? Make sure to mark the answer as the accepted solution.
If you find a reply useful, say thanks by clicking on the thumbs up button.
-- Was your question answered? Please take some time to click on "Accept as Solution" below this post. If you find a reply useful, say thanks by clicking on the thumbs up button.