
Our Community is getting an upgrade! To get everything ready for the relaunch, we’ll be placing the site in read-only mode starting September 21st.
We really appreciate your understanding while we get things set up behind the scenes. Catch up on all the exciting details about the move here.
Need help or have questions? Drop us a line at [email protected]

Support Questions
 Hi, I'm CLEO! Something exciting is coming to the Community. Stay Tuned!
- Cloudera Community
- Support
- Support Questions
- Nifi registry issue with https
- Subscribe to RSS Feed
- Mark Question as New
- Mark Question as Read
- Float this Question for Current User
- Bookmark
- Subscribe
- Mute
- Printer Friendly Page
- Subscribe to RSS Feed
- Mark Question as New
- Mark Question as Read
- Float this Question for Current User
- Bookmark
- Subscribe
- Mute
- Printer Friendly Page
Nifi registry issue with https
- Labels:
-
Apache NiFi
-
NiFi Registry

Created 10-18-2023 07:58 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I have enabled https on nifi registry properties and generated key store and trust store using tls toolkit and added in the properties file. I am able to start nifi registry on port 18443 and host 0.0.0.0 as it showing in logs that jetty server started on https://0.0.0.0:18443/nifi registry
my nifi registry is hosted as aks pod.
when I enable ingress for it. It’s returning me as 502 bad request.
are there any changes to be done to make my nifi registry run https.
Goal : i want to enable 2 way ssl authentication so that nifi could connect to nifi registry.


Created 10-20-2023 02:01 PM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@Knowledgeknow
I am not clear here:
when I enable ingress for it. It’s returning me as 502 bad request
NiFi-Registry is secured once configured with an HTTPS hostname, HTTPS port, keystore, and truststore. For more info: security_configuration
As soon as HTTPS is enabled, TLS/SSL is used. It is either enabled as "REQUIRED" or "WANT", but can not be set to "NONE". This is controlled by
nifi.registry.security.needClientAuth=true (default)
With "true" being "Required" and false being "Want"
In order for NiFi to be able to successfully negotiate a mutual TLS handshake, the NiFi "registry client" must use the HTTPS nifi-registry "https://<nifi-registry hostname>:<port> url and have either the keystore and truststore configured in nifi.properties or a StandardRestrictedSSLContextService configured with valid keystore and truststore.
The NiFi-registry keystore must:
- Contain a single PrivateKeyEntry
- PrivateKey entry has serverAuth EKU
- PrivateKey Entry has SAN entries that include any hostname and IPs that client(s) may use to connect to it. Since you have configured hostname with 0.0.0.0 so that NiFi-Registry binds to all NICs, you'll need to make sure valid network IPs and hostnames are in the SAN.
The NiFi-Regsitry truststore must:
- Contain the complete trust chain capable of establish trust for the PriavteKey in the NiFi keystore being used by the NiFi Registry Client.
The NiFi keystore must:
- Contain only one PrivateKey Entry.
- PrivateKey DN must not use wildcards
- PrivateKey Entry MUST have both clientAuth and ServerAuth EKU
- PrivateKey Entry must have SAN entries for NiFi hostname, and IPs clients may use to connect to it.
The NiFi truststore must:
- Contain the complete trust chain capable of establish trust for the PriavteKey in the NiFi-Registry keystore configured in the nifi-registry.properties file.
If you found any of the suggestions/solutions provided helped you with your issue, please take a moment to login and click "Accept as Solution" on one or more of them that helped.
Thank you,
Matt
Created 11-01-2023 06:17 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
- Does your NiFi Keystore meet the following requirements?
- MUST contain only one PriavteKey Entry
- PrivateKey Entry must include ExtenedKeyUsage(EKU) for both clientAuth and serverAuth.
- PrivateKey Entry DistinquishedName (DN) does not contain wildcards
- PrivateKey Entry contains one of more SubjectAlternativeName (SAN) entries that includes the hostname and IP for the NiFi server on which it will be used.
2. Sounds like you have configured nifi.properties:
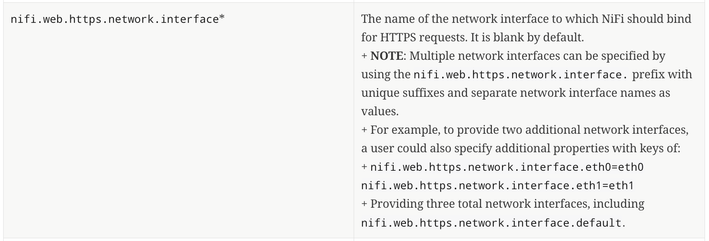
nifi.remote.input.host=0.0.0.0While this will work for a http setup, it will cause issue with the TLS handshake. Instead this should set the hostname of the NiFi server and the hostname must be a SAN entry. If you are trying to have your NIFi bind to multiple Network Interface Cards (NICs) then you should use the "nifi.web.https.network.interface*" properties in web properties section of the nifi.properties file.
If you found any of the suggestions/solutions provided helped you with your issue, please take a moment to login and click "Accept as Solution" on one or more of them that helped.
Thank you,
Matt
Created 02-02-2024 10:58 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@oneofthemany
You would get better traction form the community by starting a new question since this question already has an accepted solution and has nothing to do with NiFi TLS-toolkit usage.
Thank you,
Matt

Created 02-05-2024 04:18 AM
- Mark as New
- Bookmark
- Subscribe
- Mute
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
thanks, I have created a new post:
https://community.cloudera.com/t5/Support-Questions/NiFi-SAN-IP-using-toolkit-NiFI-Registry/td-p/383...

- « Previous
-
- 1
- 2
- Next »

