Nifi Security harden: Missing access policies features to achieve Multi-Tenant Authorization.
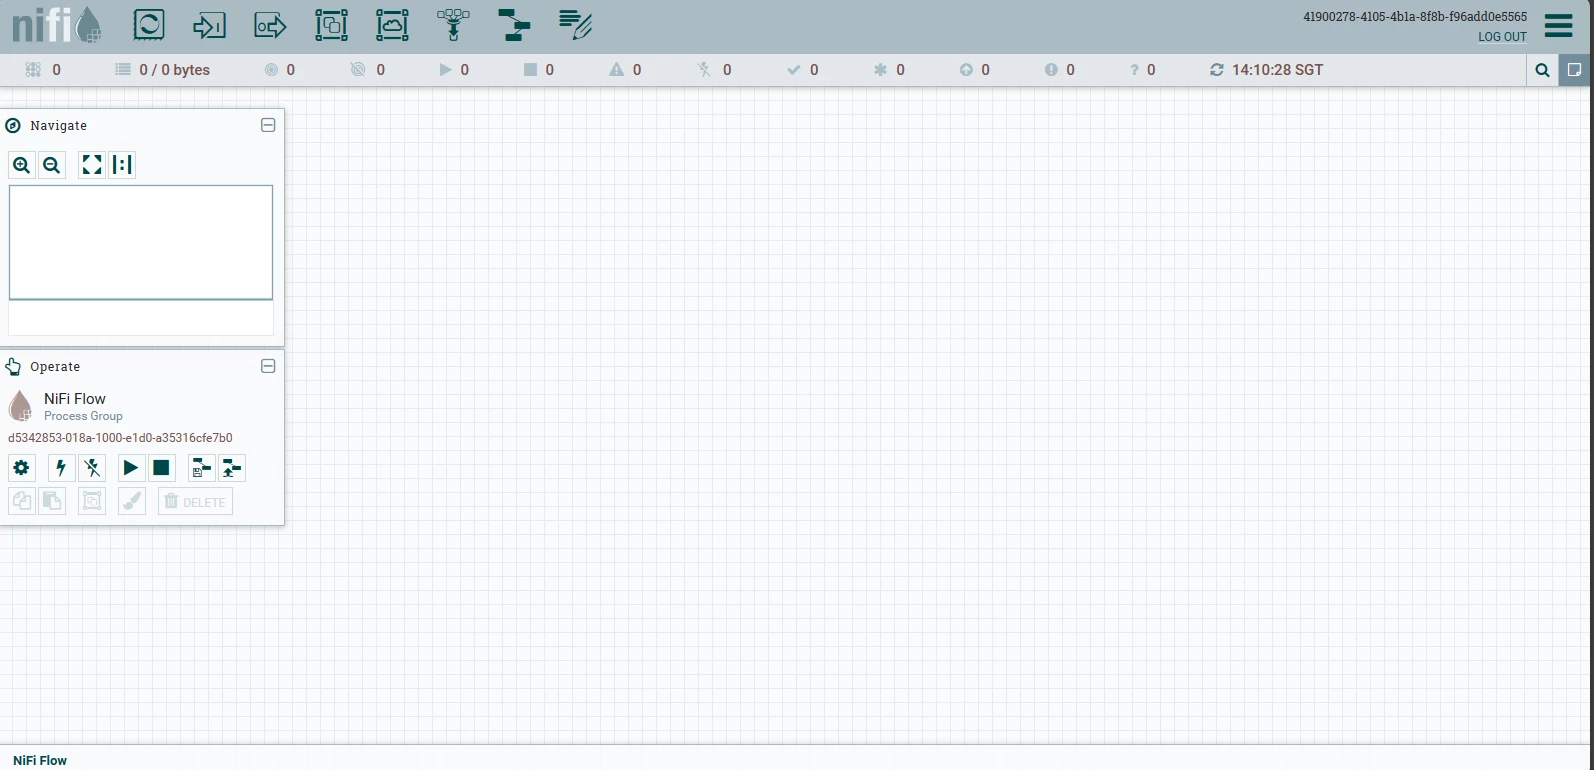
Hi, I would like to enquire about the missing access policies features as I run my nifi instance.
Step that I did:
1) Generate the certificate and key (keystore.jks, truststore.jks, nifi.properties)
Command: .\bin\tls-toolkit.sh standalone -n "localhost"
2) Copy the above 3 cert to ".\nifi-1.23.2\conf"
3) Generate the user's client certificate to authenticate to NiFi
Command: .\bin\tls-toolkit.sh standalone -C "CN=sys_admin, OU=NIFI"
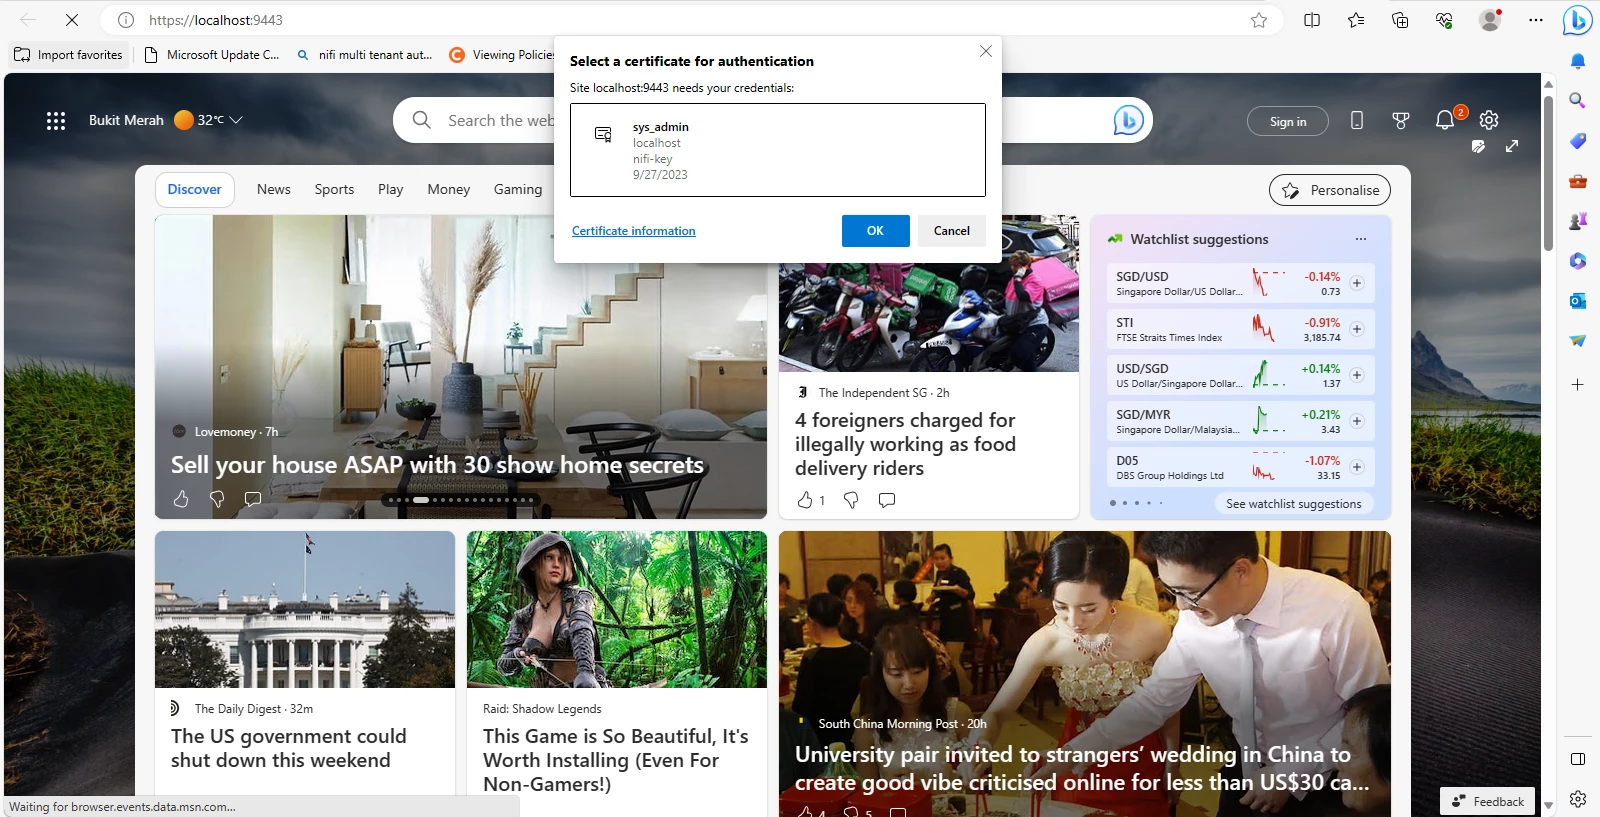
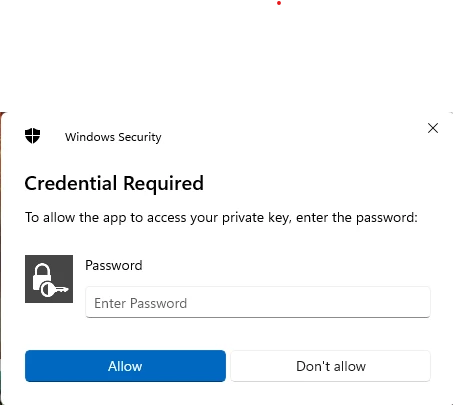
4) Load the client certificate into web browser (EDGE)
5) Populate the Initial Admin Identity
Open authorizers.xml in ".\nifi-1.23.2\conf"
In UserGroupProvider section, replace <property name = "Initial User Identity 1"><property> to <property name = "Initial User Identity 1">CN=sys_admin, OU=NIFI<property>
In accessPolicyProvider section, replace <property name = "Initial Admin Identity"><property> to <property name = "Initial Admin Identity">CN=sys_admin, OU=NIFI<property>
6) Start NiFi
Command: ,\bin\run-nifi.bat
7) Open Web browser to https://localhost:9443/nifi